
The ISO 27001 Challenge
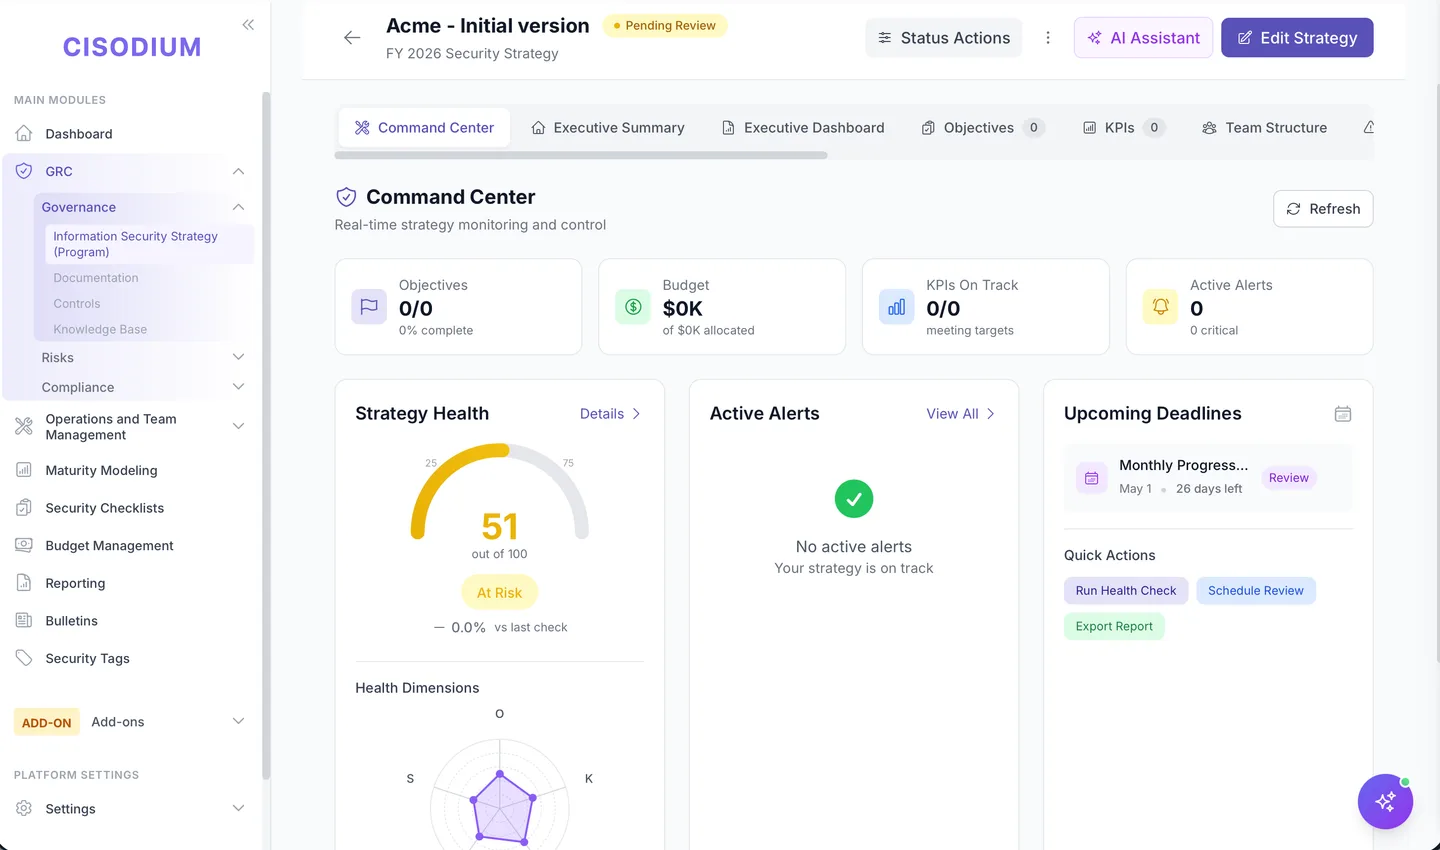
Managing ISO 27001 with spreadsheets means months of manual evidence collection, version chaos across shared drives, and audit-season panic. Most organizations spend 6-12 months preparing for certification — and then struggle to maintain it.
How Cisodium Simplifies ISO 27001
From initial gap analysis to ongoing surveillance audits — every step covered.
Control Mapping — 93 Annex A Controls
All 93 Annex A controls from ISO/IEC 27001:2022 come pre-mapped. Link each control to your policies, risks, assets, and responsible owners. When a control changes status, every linked entity updates automatically through Cisodium's entity linking system.

Automated Evidence Collection
Connect 300+ integrations to automatically collect compliance evidence — access reviews from IAM providers, vulnerability scan results, configuration snapshots, training records. Every artifact is version-controlled with timestamps and audit trail.

Audit Cycle Management
Plan internal and external audit cycles, assign auditors, track findings by severity, manage corrective actions with deadlines, and monitor closure rates. Each finding gets a unique tag (FND-XXXXX) linked to the affected control and risk.

Gap Analysis & Readiness Score
See your ISO 27001 compliance score in real-time. Identify gaps before the auditor does — broken down by Annex A domain (A.5 Organizational, A.6 People, A.7 Physical, A.8 Technological). Generate readiness reports for management review.

Risk Management — Clause 6.1
ISO 27001 Clause 6.1 requires a formal risk assessment process. Cisodium provides quantitative risk analysis with heat maps, inherent vs. residual scoring, bow-tie analysis, financial exposure modeling, and treatment plans linked directly to Annex A controls.

Continuous Improvement — Clause 10
Demonstrate ongoing improvement to auditors with maturity scoring, KPI tracking, trend analysis, and strategic objectives. Track your ISMS maturity over time and generate evidence of the Plan-Do-Check-Act cycle that auditors expect to see.
Beyond Compliance — The ISMP Advantage
ISO 27001 is one framework. Your security program has 14+ domains. With Cisodium, your ISO 27001 controls automatically connect to everything else.
One control links to your entire security program
CTRL-00042 (Access Control) → linked to RISK-00099 → triggered by INCD-00034 → tracked in AUDT-00001 → reported to the board
 NIST CSF
 SOC 2
 GDPR
 PCI DSS
 CMMC
 C2M2
Ready to simplify your ISO 27001 journey?
See how Cisodium maps all 93 Annex A controls, automates evidence collection, and keeps you audit-ready year-round.
Request demo