Beyond GRC.
Meet the ISMP.
Every security domain — risk, compliance, incidents, budget, strategy — unified in one platform built for operations, not audits.
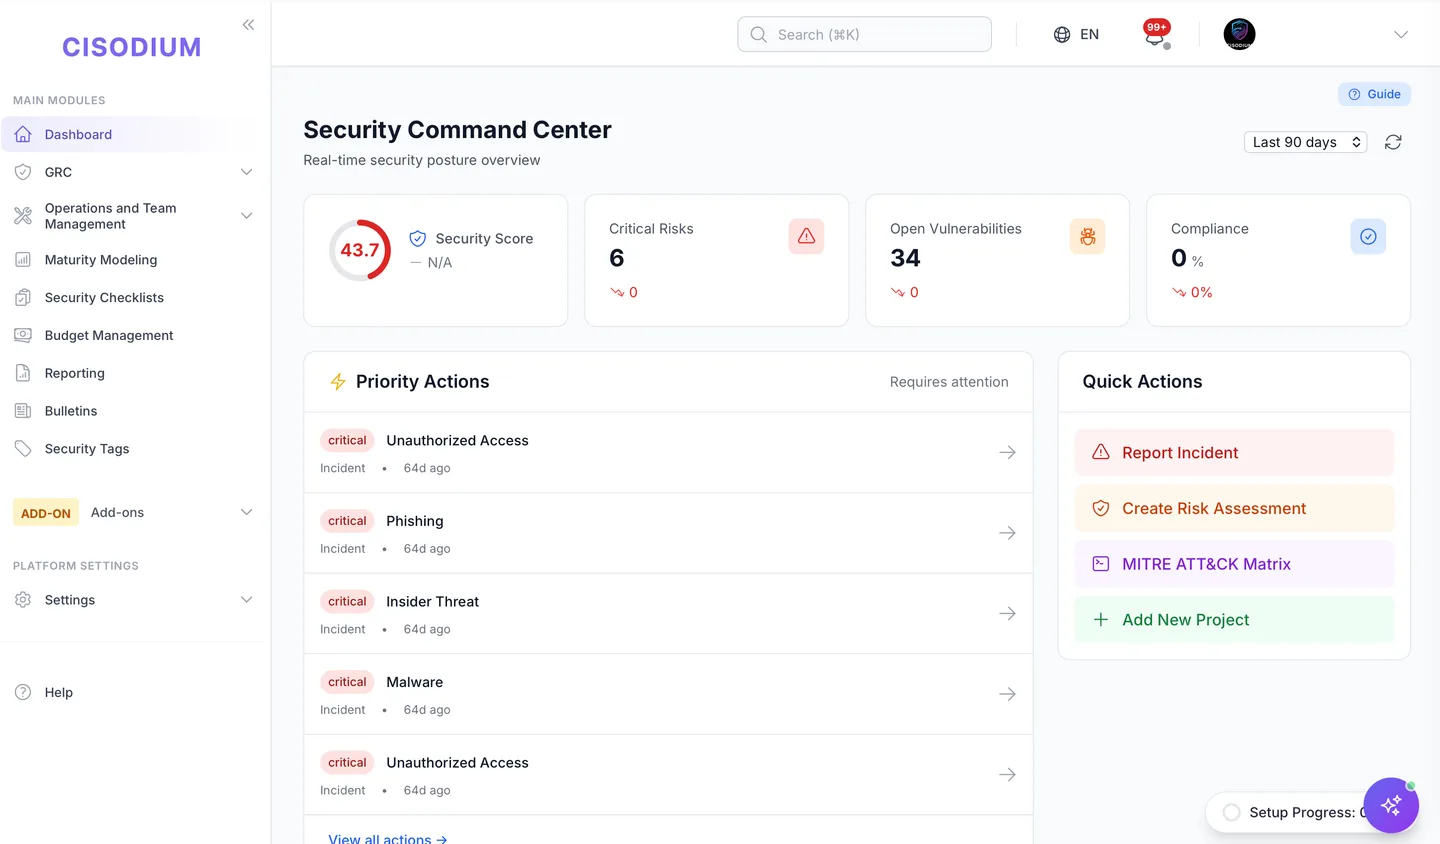
Compliance = Security.
You can pass every audit and still get breached. Legacy GRC tracks paperwork — not your operational reality.
Organizations using 5+ disconnected security tools spend 40% more time on integration than on actual security work.
Every domain.
One platform.
Twenty domains run on one register of assets, risks, controls and people — so what happens in one shows up everywhere it matters.
- Security StrategyObjectives · KPIs · board reports
- Risk ManagementRegisters · residual risk · treatment
- Policy & DocumentsDraft → approve → retire
- Budget & ResourcesVendors · ROI · approvals
- Compliance & FrameworksOne control, many standards
- Maturity AssessmentC2M2 · CMMC · SAMM
- Metrics & KPIsDashboards · trend analysis
- Privacy ManagementRoPA · DSAR · DPIA · consent
- Asset ManagementClassification · dependencies
- Identity & AccessAccess reviews · privileges
- Application SecurityScans · findings · SSDLC
- Hardening & Defence in DepthBaselines · layered controls
- SOC OperationsCases · shifts · SIEM
- Incident ManagementWar room · investigations
- Vulnerability ManagementNessus · Qualys · Rapid7
- Exposure ManagementAttack surface · crown jewels
- Business ContinuityBCP/DRP · BIA · RTO/RPO
- Vendor Risk (TPRM)Questionnaires · supply chain
- Training & AwarenessPhishing sims · completion
- Security ArchitectureData flows · zero trust
- Govern
- Assure
- Protect
- Detect & respond
- Resilience
One finding, followed across the platform
VLN-00089Vulnerability foundAST-00234On a critical assetRISK-00099Raises a riskCTRL-00102Tested by a controlCMP-00012Maps to ISO 27001 A.8.8TASK-00567Fix assigned
Built for the security team.
Useful to everyone else.
Security work touches every desk. Each person gets the part that is theirs — and the rest of the program stays out of their way.
- Board & executivesPosture on one page.
A board report and a security score that explains itself — in business terms, with the trend behind it.
Reporting · Board - CISO & security teamThe whole program, one workflow.
Risks, controls, incidents and vulnerabilities in one place, and ELSA answering from your own data.
Dashboard · ELSA - Managers & risk ownersDecisions, not chasing.
Access reviews, risk acceptances and approvals arrive as tasks, with the context needed to decide.
Access reviews · Tasks - IT & operationsFixes, grouped and ranked.
Vulnerabilities grouped into fix tickets, hardening baselines and device checks — worst first.
Vulnerabilities · Hardening - DevelopersSecurity inside the release.
AppSec findings, SBOMs and release gates per project, fed straight from the pipeline.
AppSec · SBOM - HR & team leadsKnow who covers what.
Org chart, skills matrix, one-to-ones and absences — and the skills only one person holds.
Team management - Legal, privacy & procurementObligations under control.
Records of processing, DSARs and DPIAs, regulatory obligations and vendor questionnaires in one register.
Privacy · TPRM · Obligations - Every employeeShort, relevant, done.
Assigned training and phishing simulations, policies to read and acknowledge, and only the tasks that are theirs.
Security awareness · Documents - Auditors & customersEvidence without email chains.
Auditors work in their own portal; customers read your Trust Center and request documents under NDA.
Auditor portal · Trust Center
Three phases.
Reactive to proactive.
Assess your real posture.
Evaluate every domain — not just the auditable ones — and establish your baseline before the auditors do.
- Maturity assessment across every domain
- Gap analysis against ISO 27001, NIST CSF
- Risk identification and scoring
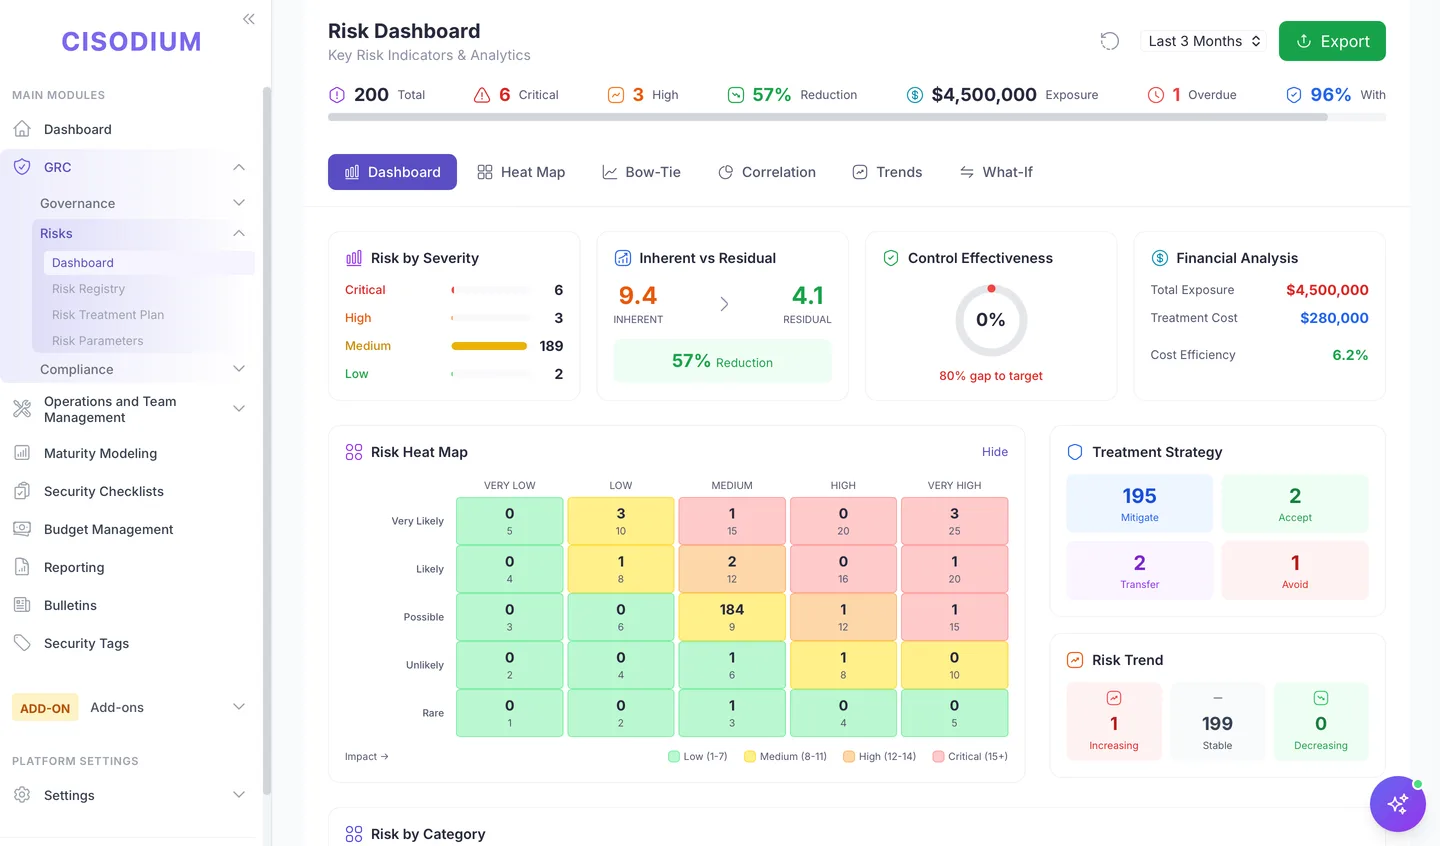
Manage from one place.
Controls, risks, compliance and operations coordinated in a single workflow — no swivel-chair integration.
- Centralized control management
- Automated compliance mapping
- Incident response workflows
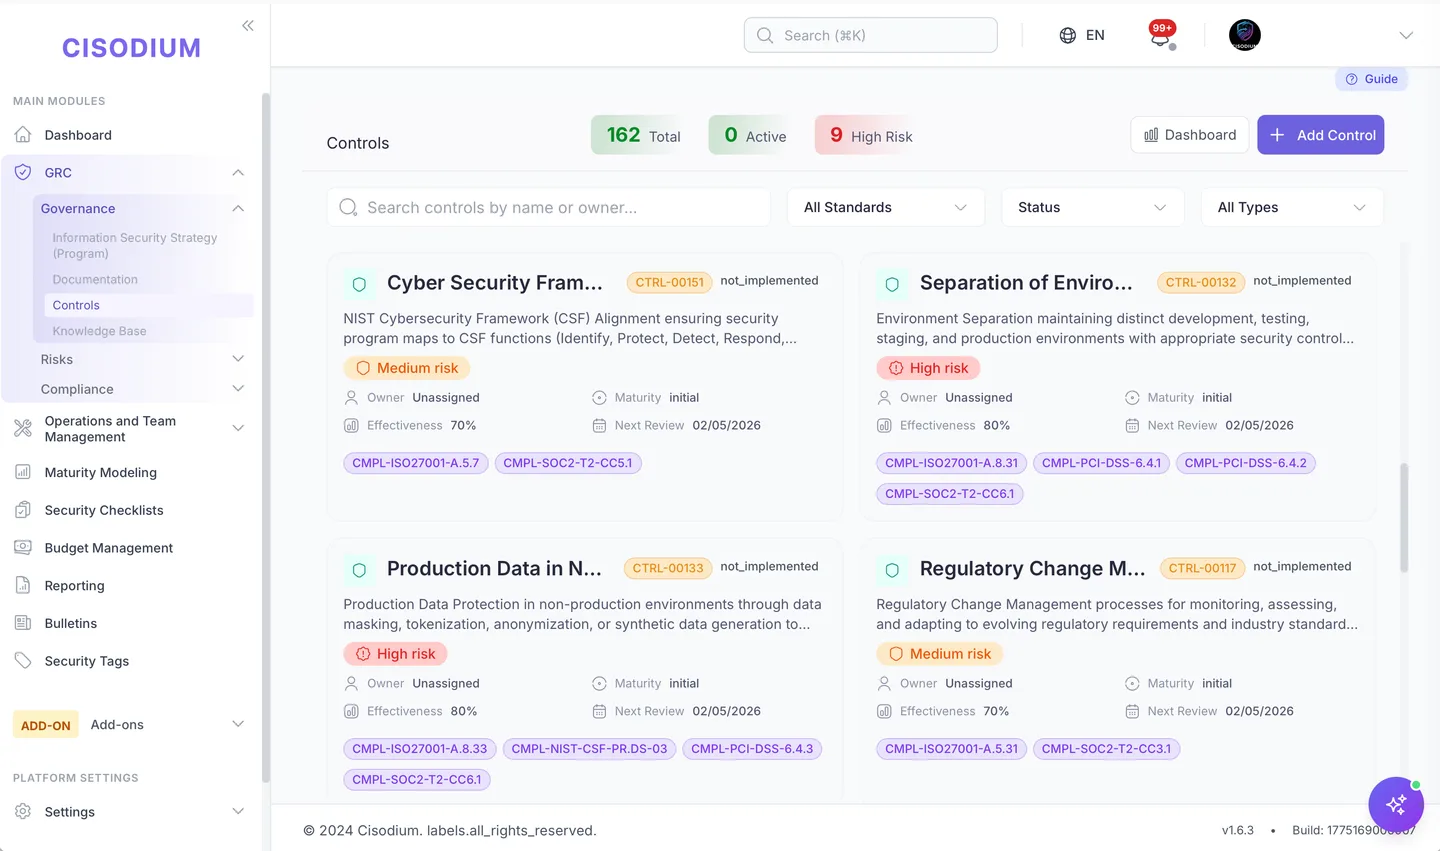
Improve with evidence.
Real-time KPIs, trends and board-ready reports. Show progress, not promises.
- Real-time security dashboards
- Continuous maturity scoring
- Board-ready executive reports
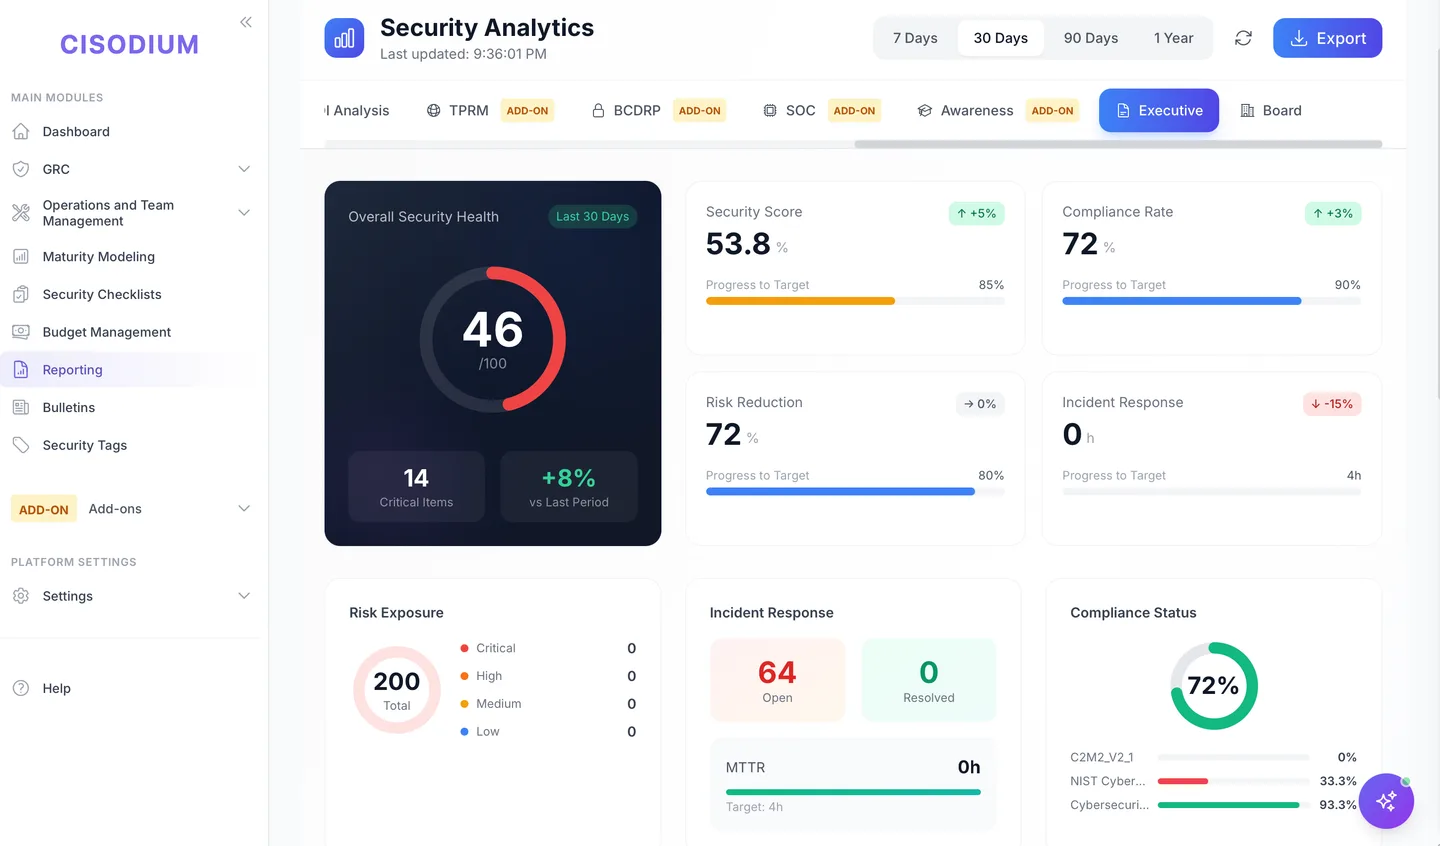
What GRC simply cannot do.
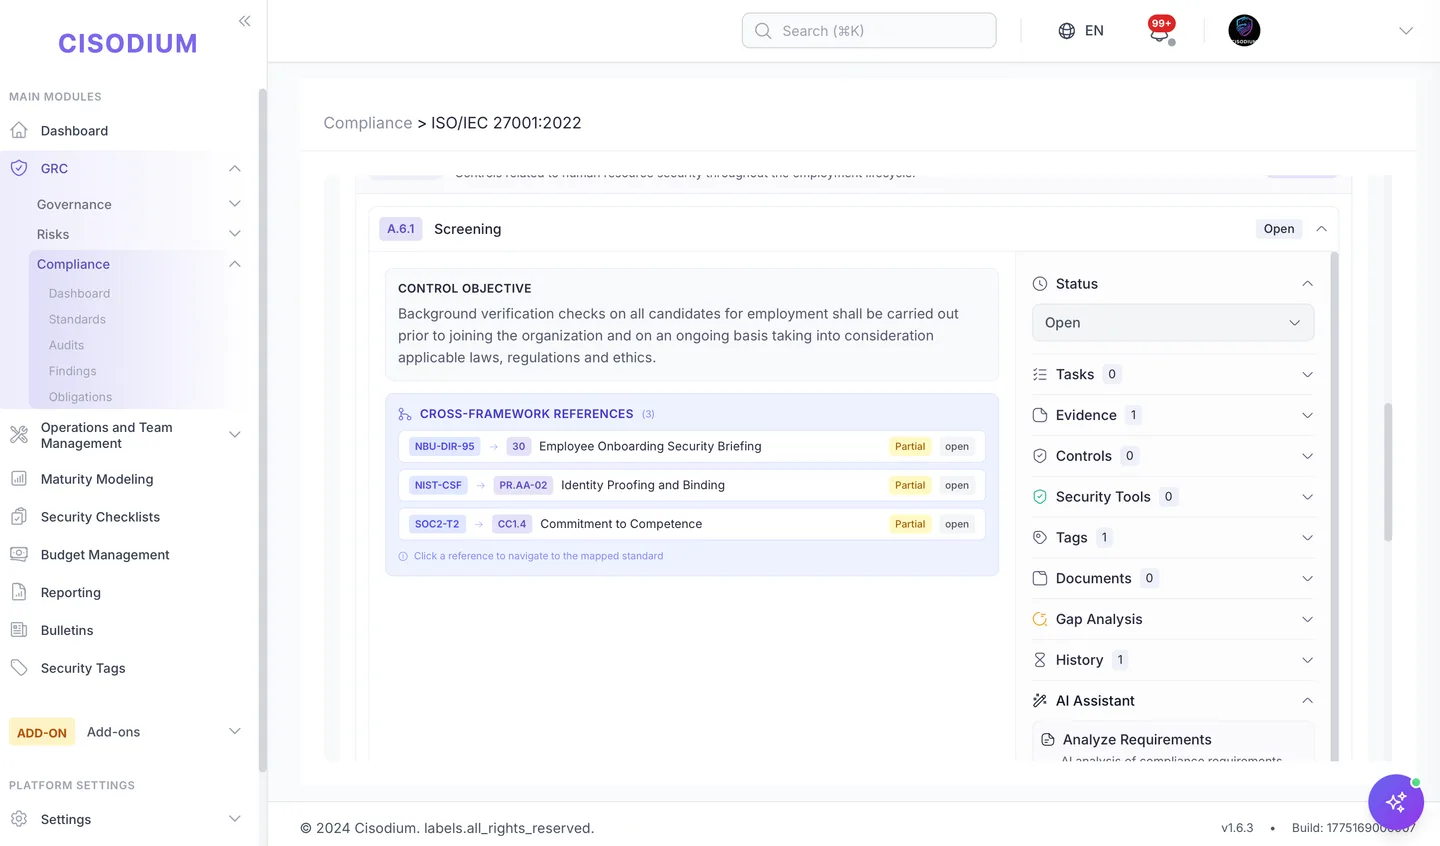
One control. Every standard.
Map a single control to ISO 27001, NIST CSF, SOC 2 and PCI DSS simultaneously — with AI gap analysis and evidence linking on one screen.
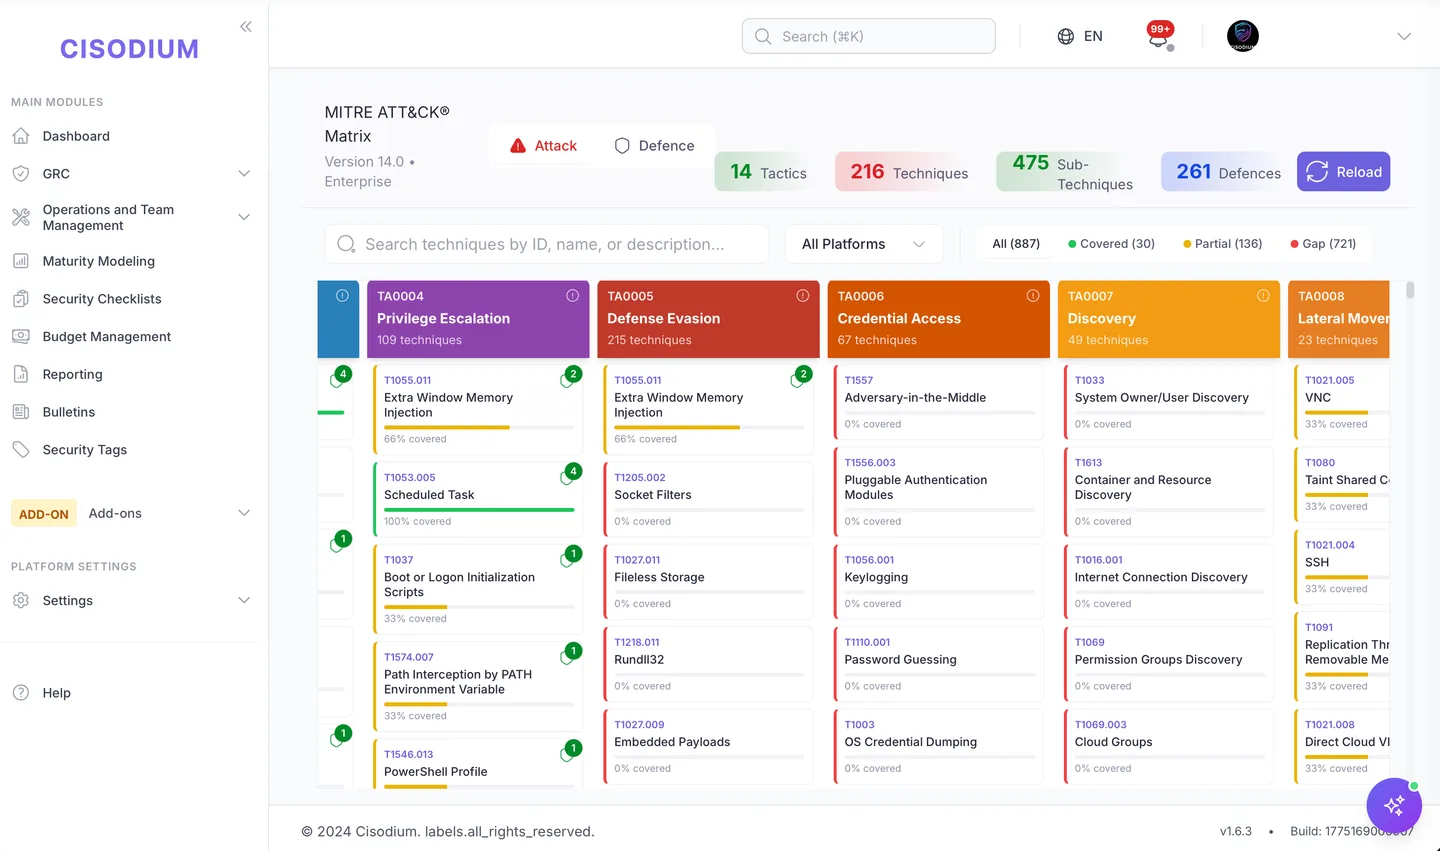
216 techniques, mapped.
Attack and Defence views across 475 sub-techniques. See gaps before attackers do.
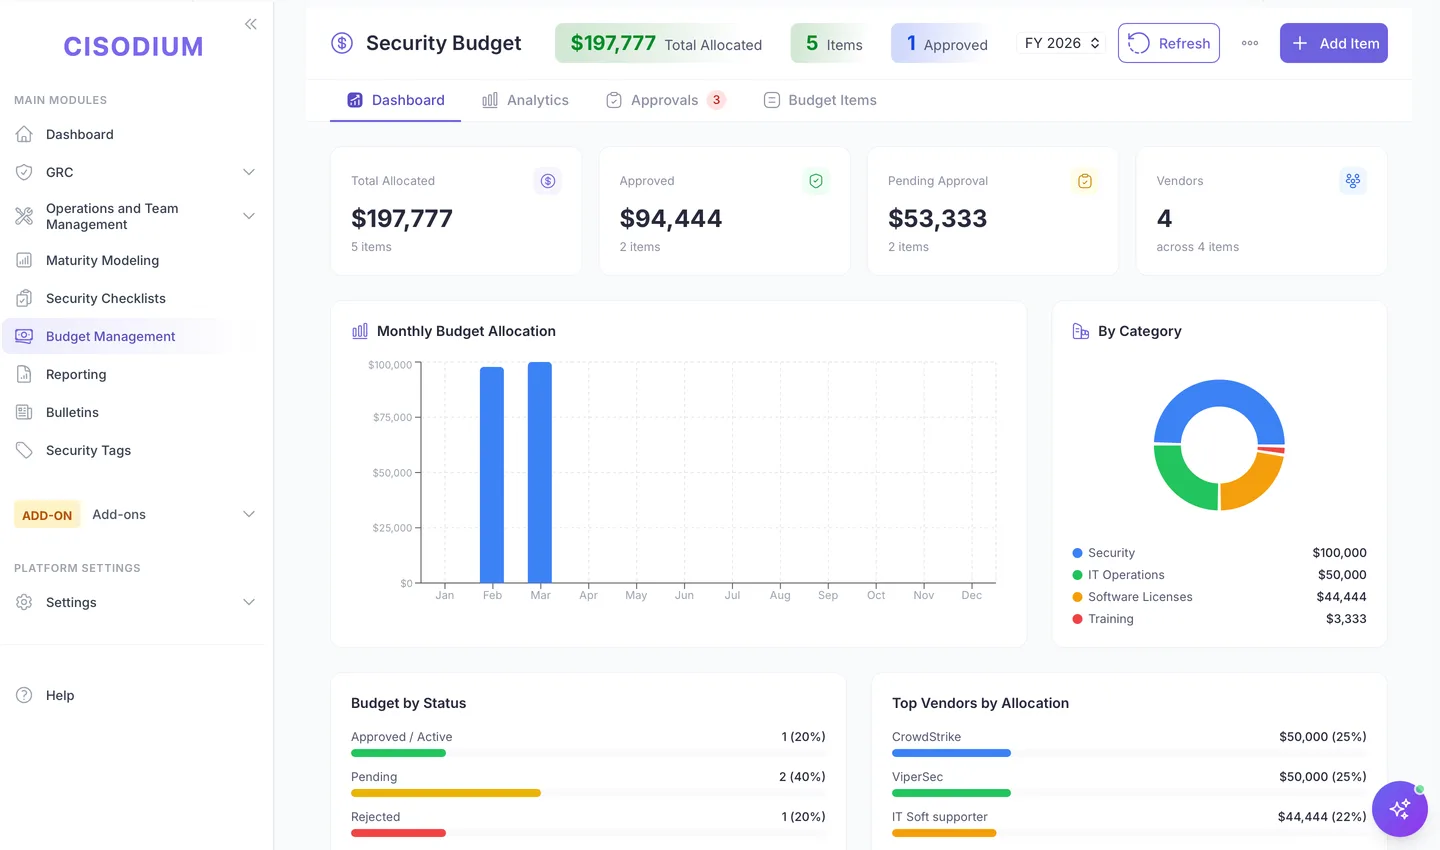
Every dollar, accounted.
Vendor breakdown, category analysis, approval workflows — a capability no GRC offers.
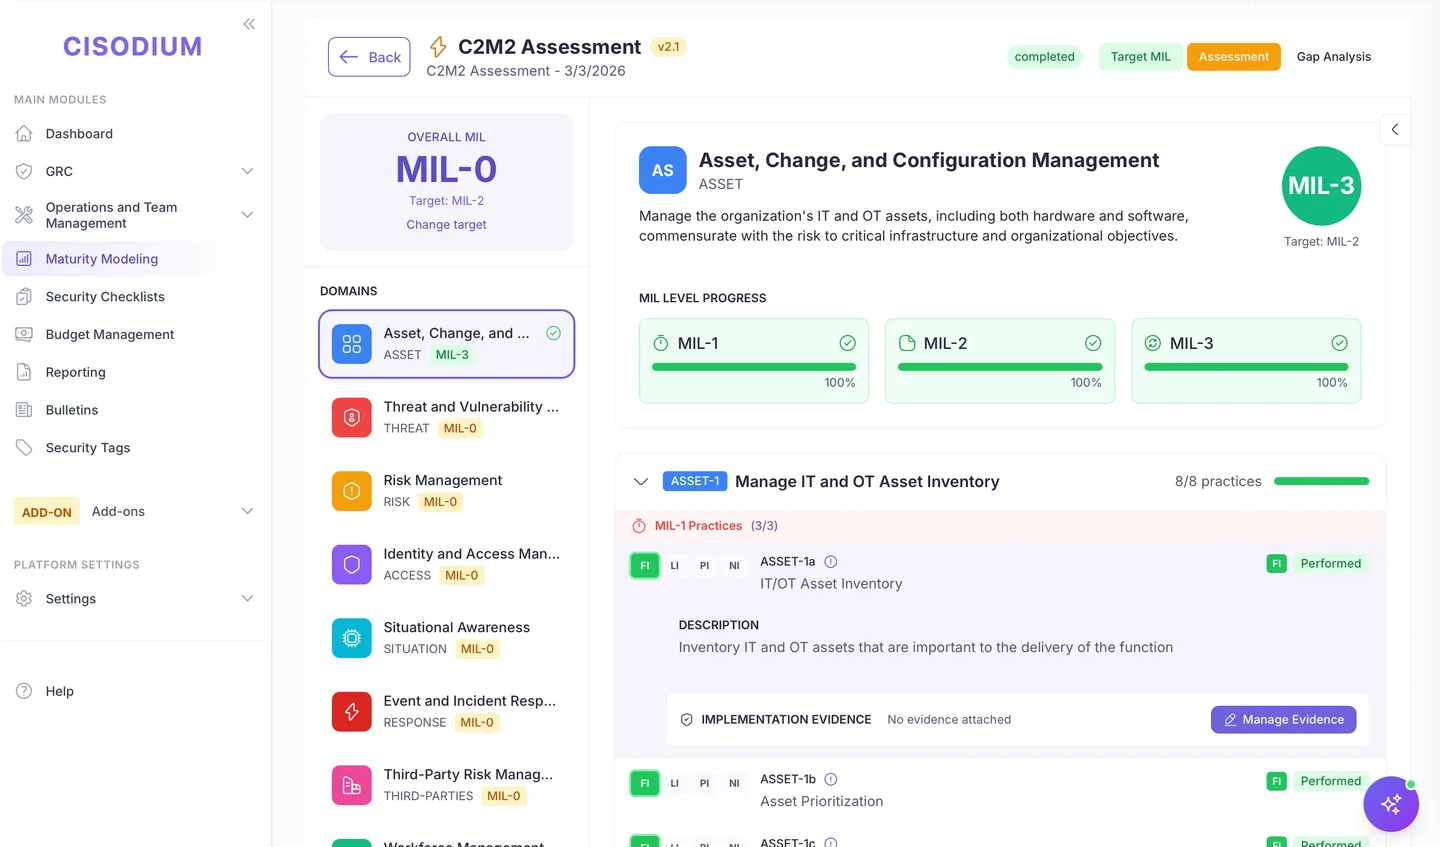
Know your gap to target.
C2M2, CMMC, NIST CSF and OWASP SAMM — MIL levels per domain, evidence per practice.
Draft to retirement.
Version control, review schedules, approvals and compliance linking for every policy.
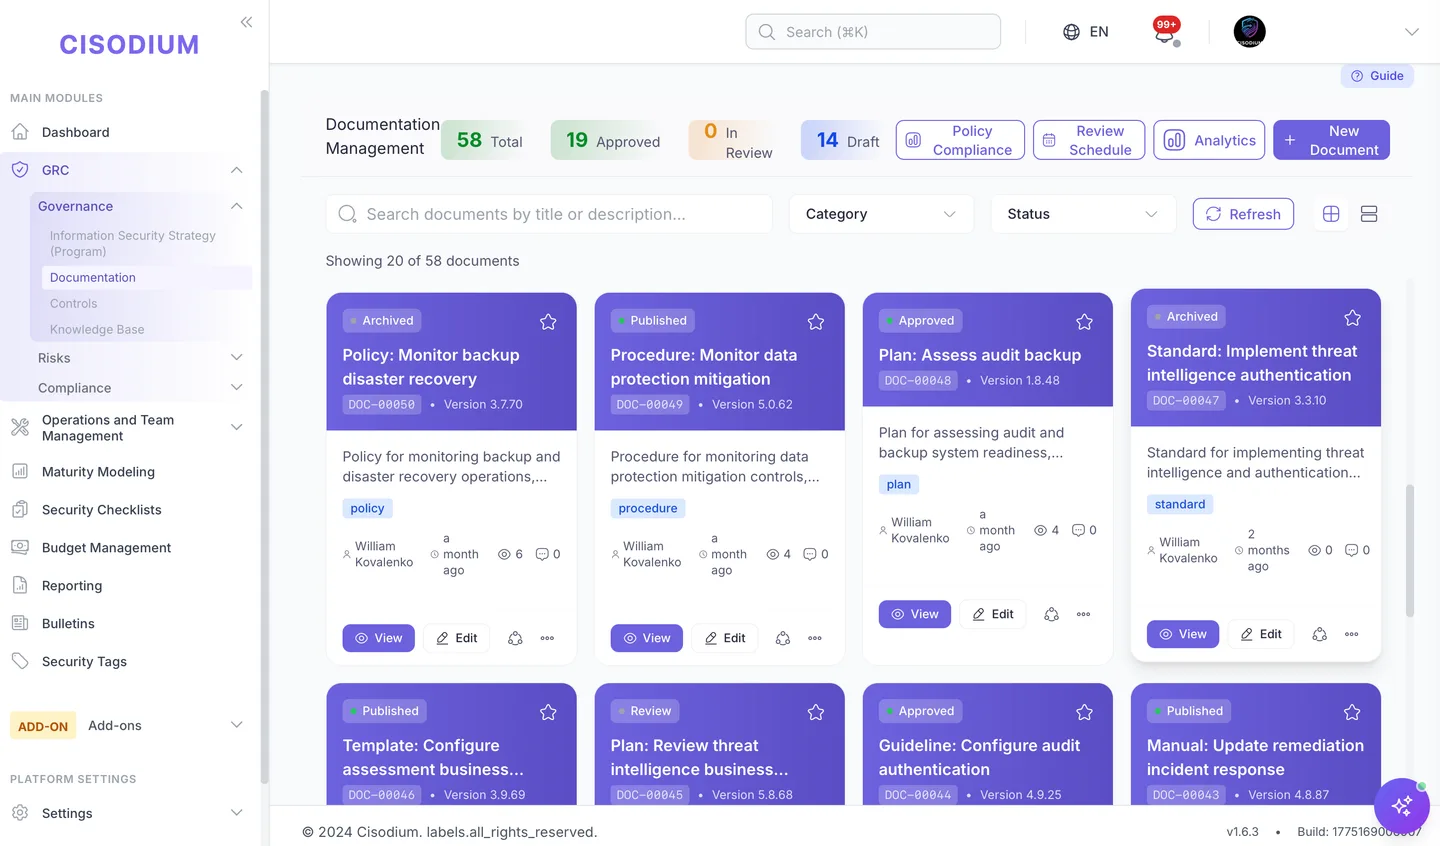
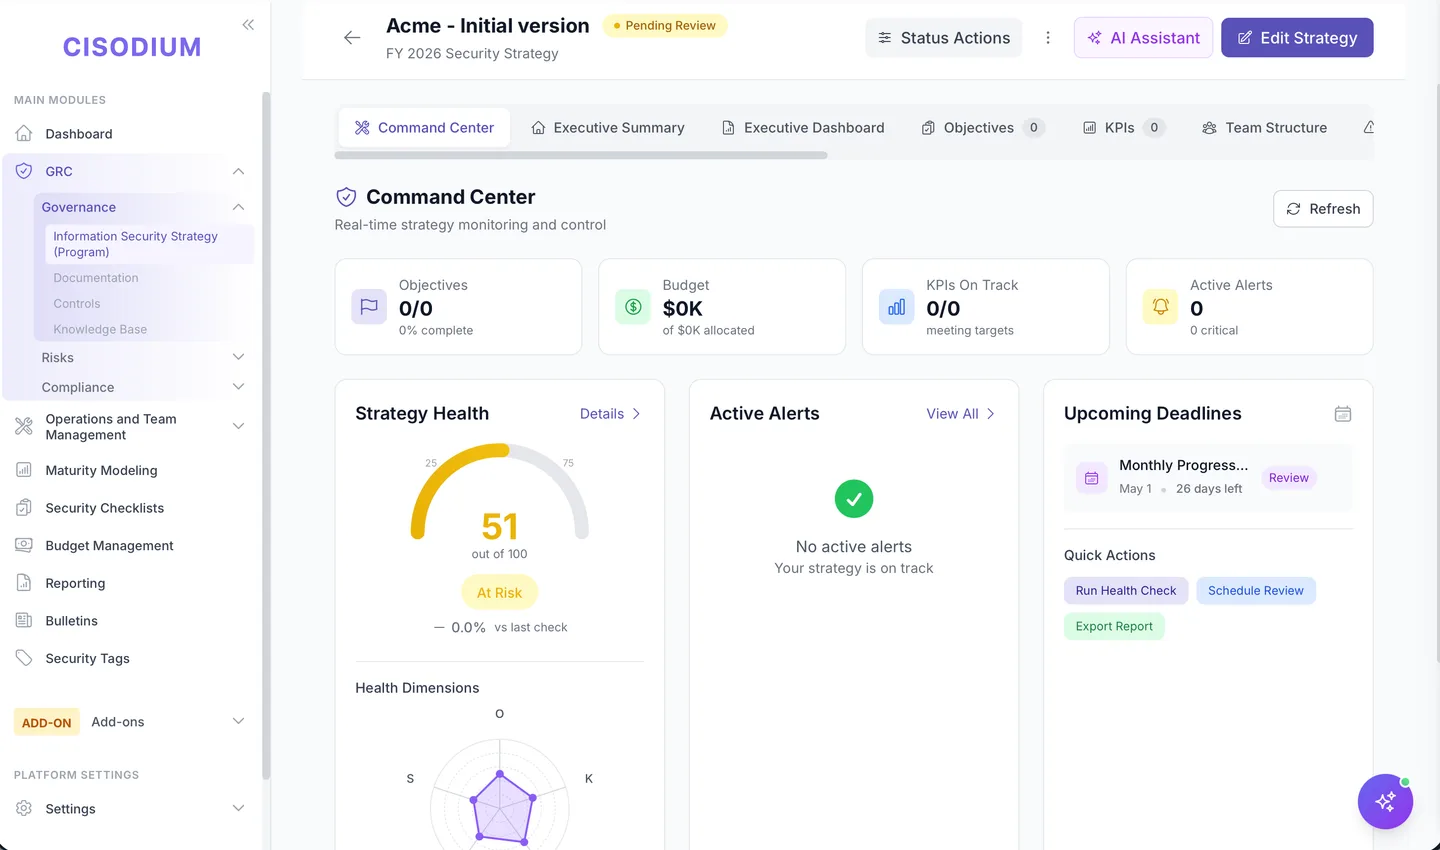
A command center, not a checklist.
Define strategic objectives, monitor strategy health in real time, track KPIs and generate executive summaries.
…and more, across every domain.
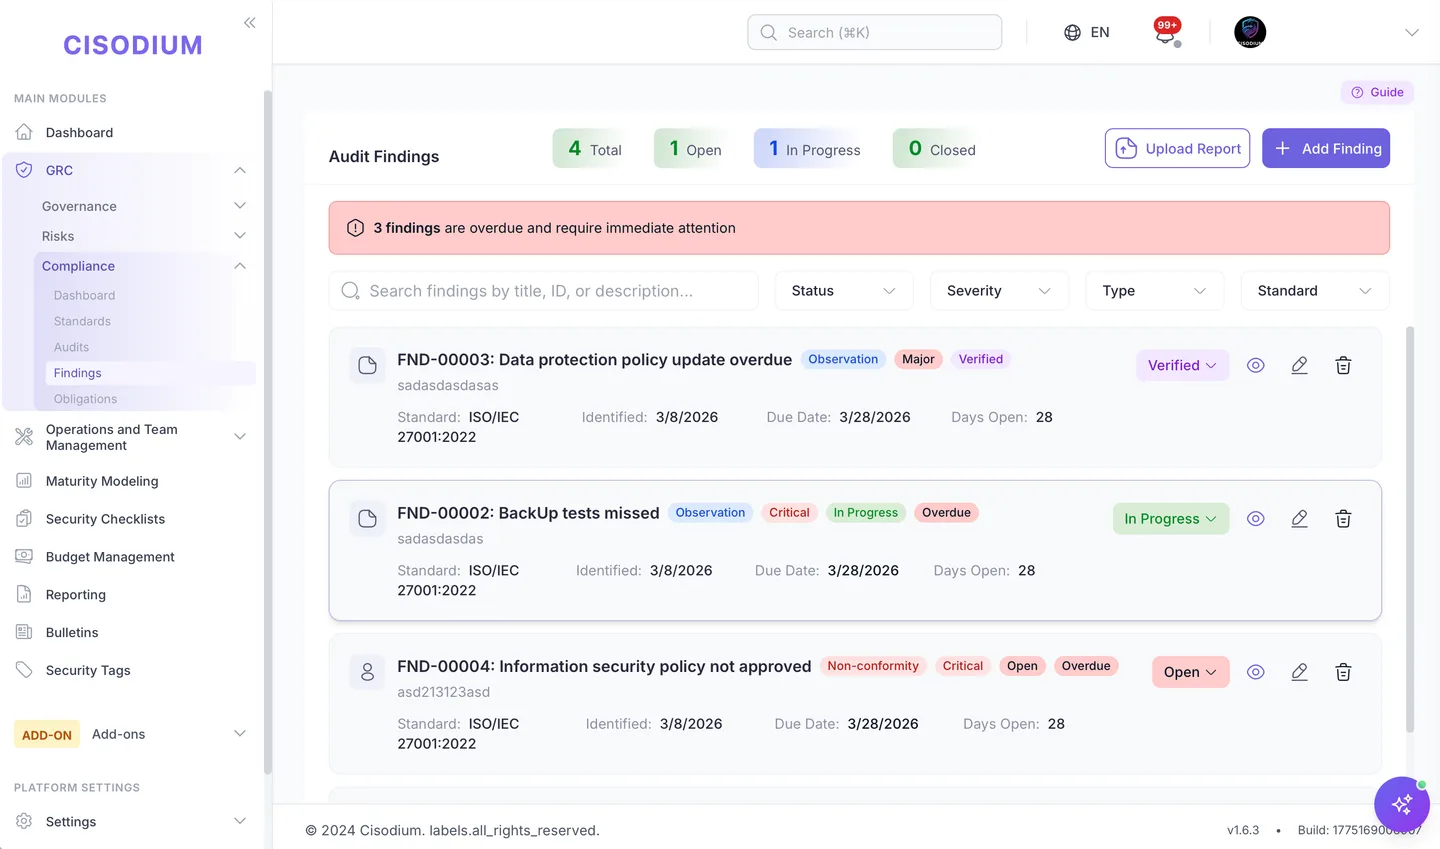
Audit findings
Track findings with severity, status and overdue alerts.
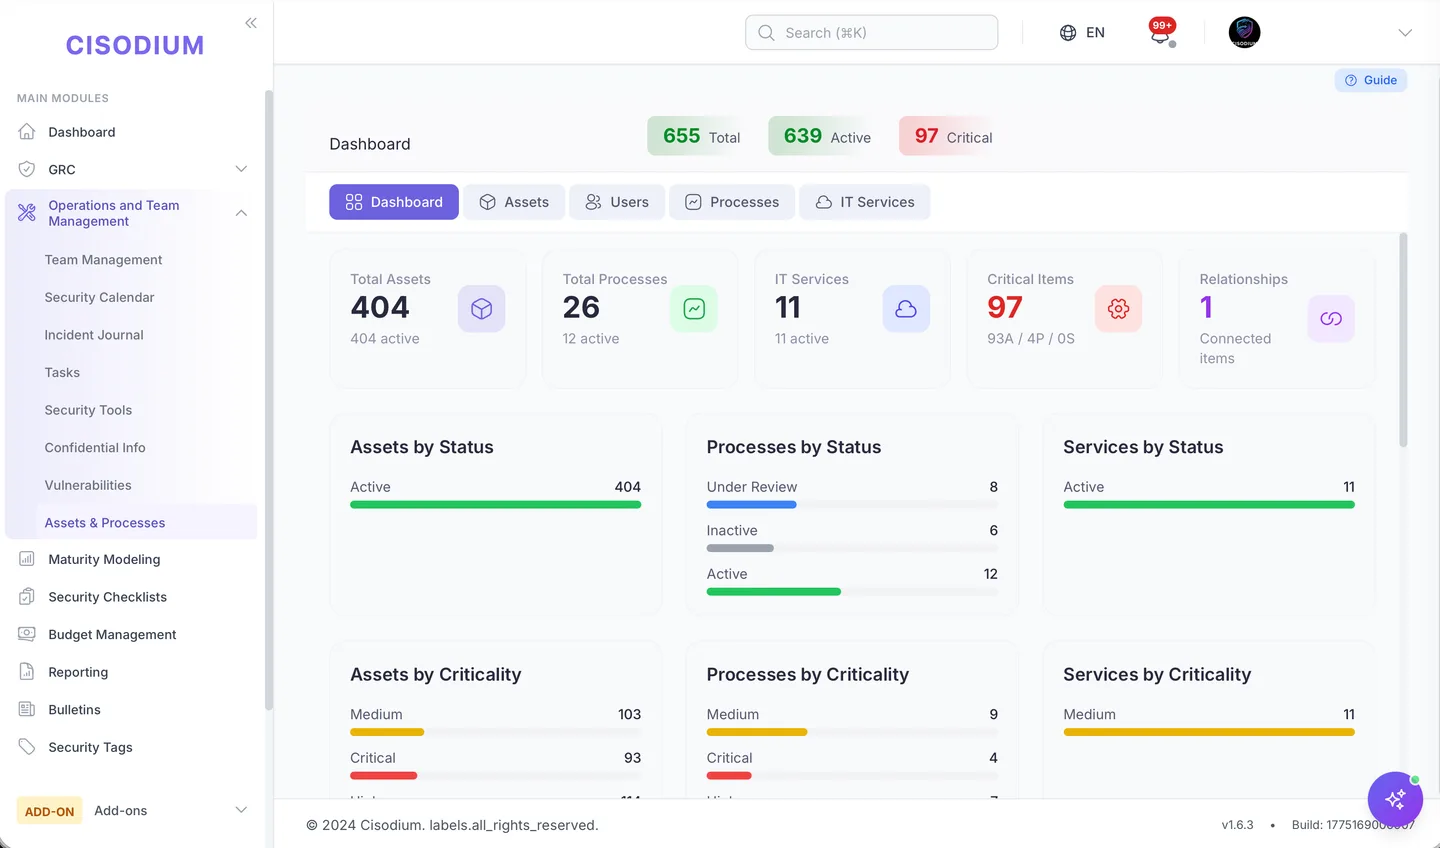
Assets & processes
Assets, processes and IT services with criticality analysis.
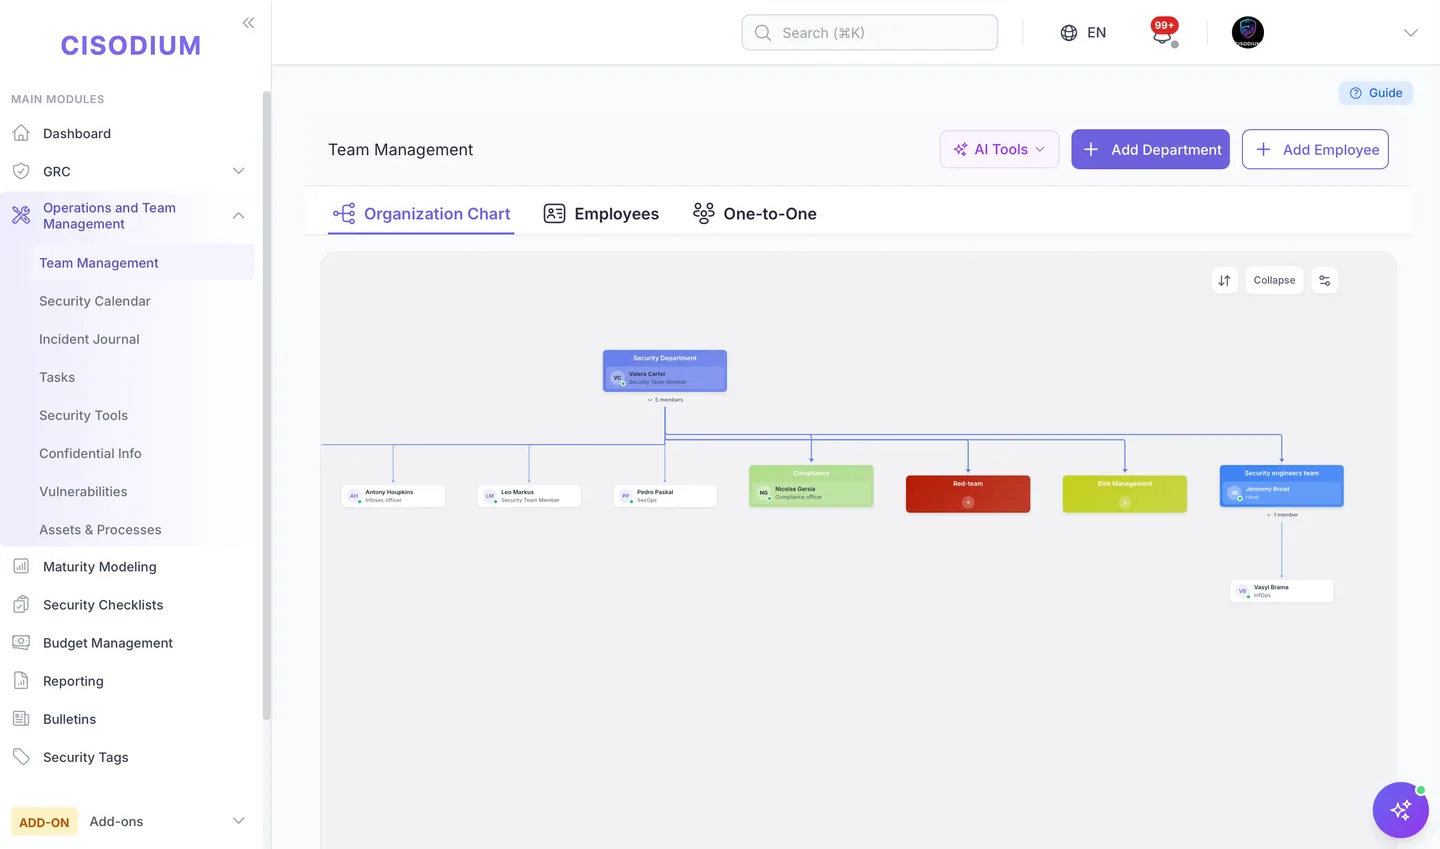
Team management
Organization chart, departments and role-based workflows.
More than a register.
Modules that do the work.
Add-ons for what a security team now answers for: AI in use, customer trust, controls tested by machine, pentests and AI agents of your own.
- AI governanceAI Shield
Finds shadow AI in the OAuth consents of Entra ID and Google Workspace, keeps one inventory of agents, copilots, LLM APIs and MCP servers, and shows ISO 42001 readiness and EU AI Act duties per system.
ISO/IEC 42001 · EU AI Act - Customer trustTrust Center
A public page on your own domain with your certifications and controls. Customers request documents under NDA and receive watermarked copies.
Own domain · NDA · Watermarked PDFs - Automated testingContinuous Compliance
Hundreds of automated tests check Active Directory, AWS, Entra ID and Microsoft 365 on a schedule, and every result lands as evidence on the controls it covers.
Active Directory · AWS · Entra ID · Microsoft 365 - Offensive testingPentest
Scope, findings and retests in one place. External testers work in their own portal: invited by email, they accept the rules of engagement first and see only their pentest, only inside its window.
External tester portal · Rules of engagement - AI agentsMCP server
Claude and other LLMs work with your program through the MCP server: they read risks, controls, assets and incidents and create records with the signed-in user's permissions — and cannot delete anything.
Model Context Protocol · OAuth · API keys - Many organizationsComing soonMSSP & company groups
One console across a service provider's clients or a group's companies: posture side by side, each organization's data kept apart.
MSSP portfolio · Company group
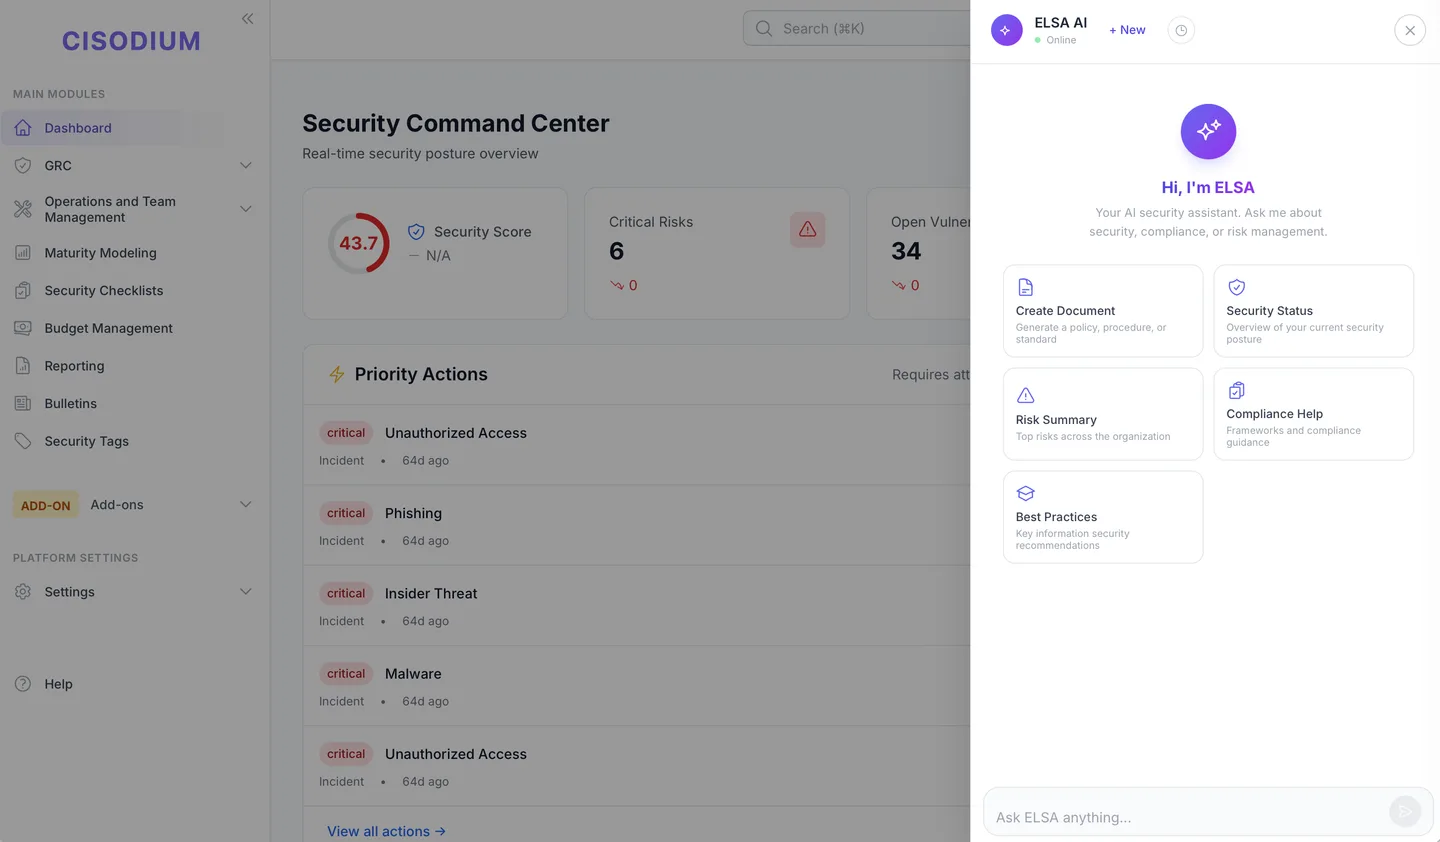
“Ask anything about your security program — ELSA answers from your actual data, not generic templates.”
One control.
Many standards satisfied.
 ISO 27001ISO/IEC 27001:2022
 NIST CSFCybersecurity Framework
 SOC 2SOC 2 Type II
 PCI DSSPayment Card Industry DSS
 GDPRData Protection Regulation
 CMMCMaturity Model Certification
 C2M2Capability Maturity Model
+ custom frameworks
Custom frameworks tailored to your industry and regulatory requirements.
0+ integrations.
 Splunk
 QRadar
 Sentinel
 Nessus
 Qualys
 Rapid7
 CrowdStrike
 AWS
 Google Cloud
 Jira
 Slack
 GitHub
SIEM & SOC
- Splunk
- QRadar
- Microsoft Sentinel
- Elastic SIEM
Scanners
- Nessus
- Qualys
- Rapid7
- Shodan
- Censys
Cloud
- AWS
- Microsoft Azure
- Google Cloud
Collaboration
- Jira
- Slack
- GitHub
- GitLab
Endpoint & Intel
- CrowdStrike
- GitGuardian
- Active Directory
…and custom API integrations for your proprietary tools.
Risk to privacy to AppSec
Splunk, Nessus, Jira, AWS…
ISO 27001 to CMMC + custom
Automation-first design
“A security platform must itself be secure — built by security professionals, with defence in depth at every layer.”
AES-256 at rest & in transit, HashiCorp Vault for credentials.
Role-based access with multi-tenant isolation.
Every action logged and traceable for forensics.
Enterprise SSO via Keycloak, SOC 2 compliant architecture.
Still wondering?
An Information Security Management Platform covers the full lifecycle of information security — not just governance, risk and compliance, but operational security, integrations, metrics, training and budgeting. GRC focuses on compliance checklists; an ISMP runs your whole program.
Yes — Cisodium is a modern cyber GRC platform, and more. Beyond governance, risk and compliance, it unifies operational security, SOC operations, vulnerability and incident management, MITRE ATT&CK coverage, metrics and budgeting into one ISMP. You get a single cyber GRC solution instead of a stack of disconnected tools.
Most organizations are up and running within 2–4 weeks, cloud-hosted or on-premises. Our onboarding team helps import existing controls, map frameworks and configure integrations from day one.
ISO 27001, NIST CSF, CMMC, C2M2, SOC 2, PCI DSS and GDPR out of the box — plus custom frameworks for your industry. Controls map to multiple frameworks simultaneously.
Yes — 300+ integrations across SIEM (Splunk, QRadar, Sentinel), scanners (Nessus, Qualys, Rapid7), ticketing (Jira), communication (Slack) and cloud (AWS, Azure, GCP), plus custom APIs.
Yes. It scales from teams of 2–3 professionals to enterprise departments — automation helps small teams accomplish more, and the Starter plan covers the essentials.
Cisodium is built by security professionals with security at its core. All data is encrypted at rest and in transit, with granular RBAC, full audit logging, SSO via Keycloak and multi-tenant isolation. Credentials live in HashiCorp Vault or AES-256 encrypted storage.
A 14-day free trial with full access to all Professional plan features. No credit card required.
Ready to move
beyond legacy GRC?
14-day free trial. No credit card. Cloud or on-premises.