The whole team. One platform.
Same platform, 16 jobs. What each person on a security team actually does in Cisodium — and what changes when they do it here.
Run the programme
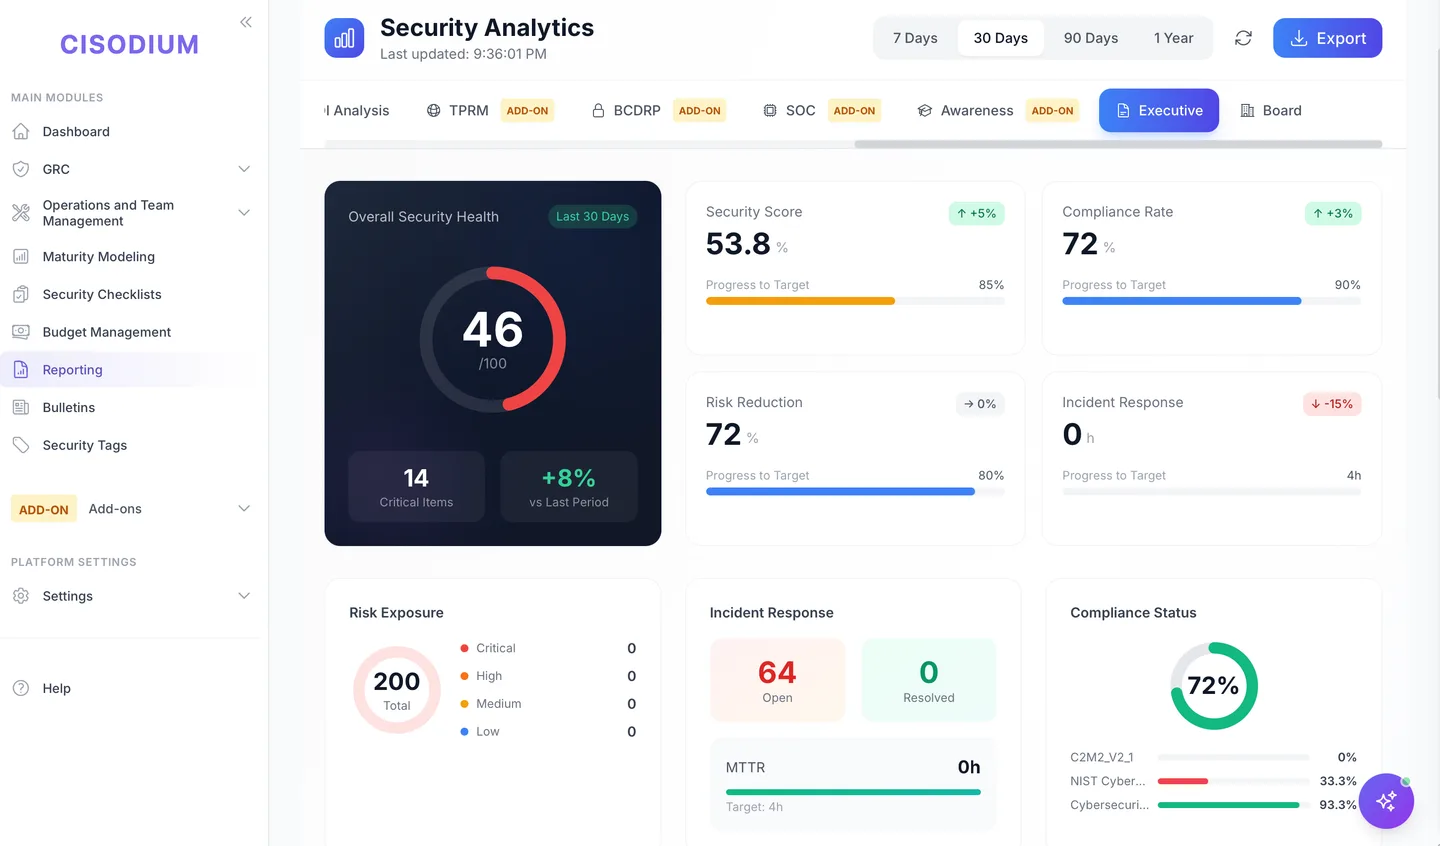 STRATEGYCISOThe board wants numbers. You'll have them.Four teams, four numbers, one board meeting. Here the board pack, the maturity grade, the budget line and the permission matrix all read off the data your team already works in.
 OPSSecurity ManagerNothing falls through the cracks.Own the operational day: the vulnerability queue, incidents from triage to lessons learned, access certifications, hardening sign-offs and phishing rounds. Each carries an owner, a date and a record behind it.
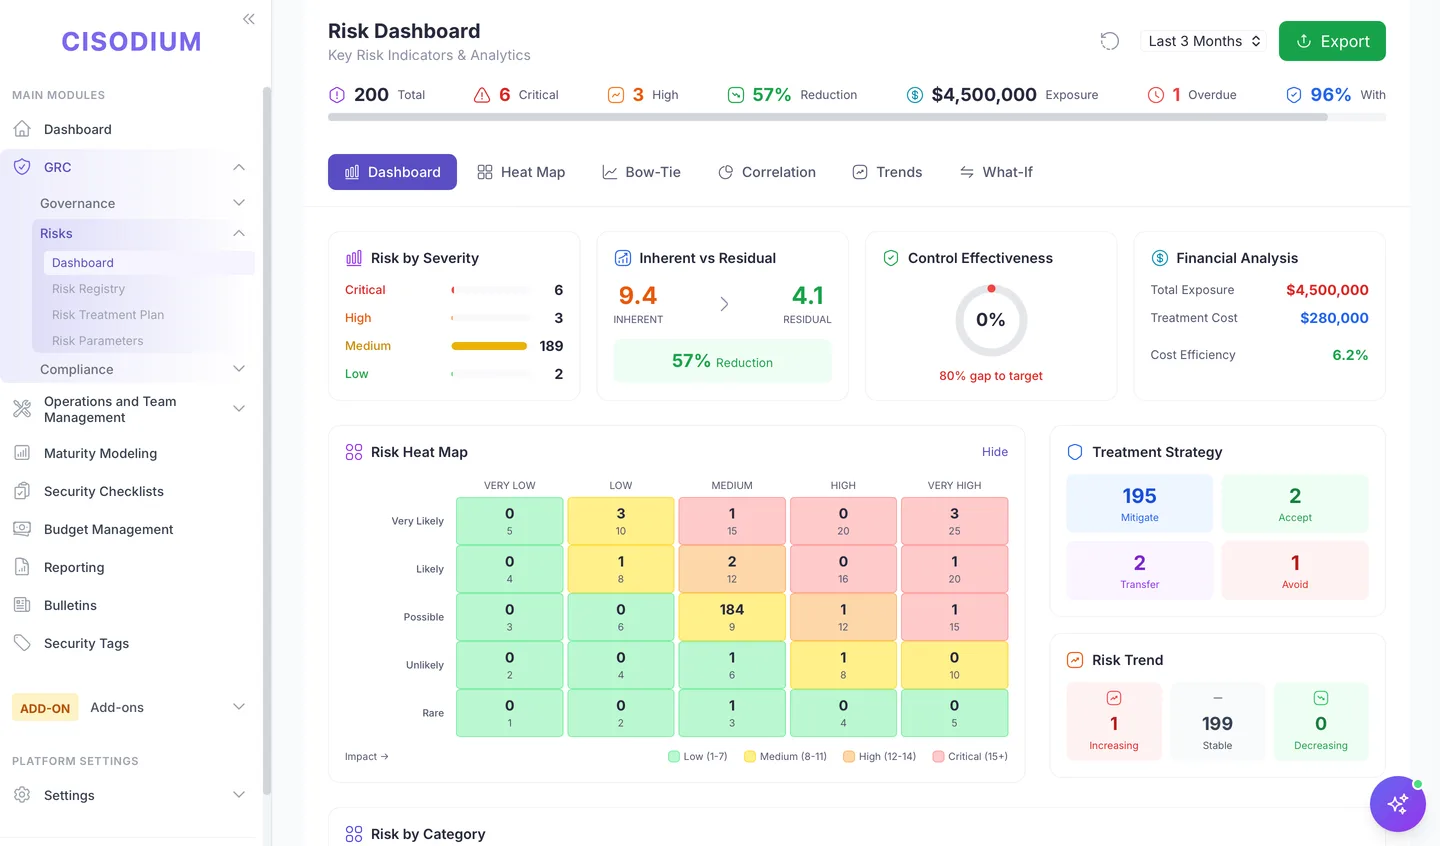 RISKRisk ManagerRisk as a strategy, not a checkbox.Spreadsheet registers miss the connections. Set the scoring methodology once, then let every entry hold the controls, processes, incidents, KRIs and vulnerabilities it actually touches, with treatment plans and formal acceptances on the record.
Prove it
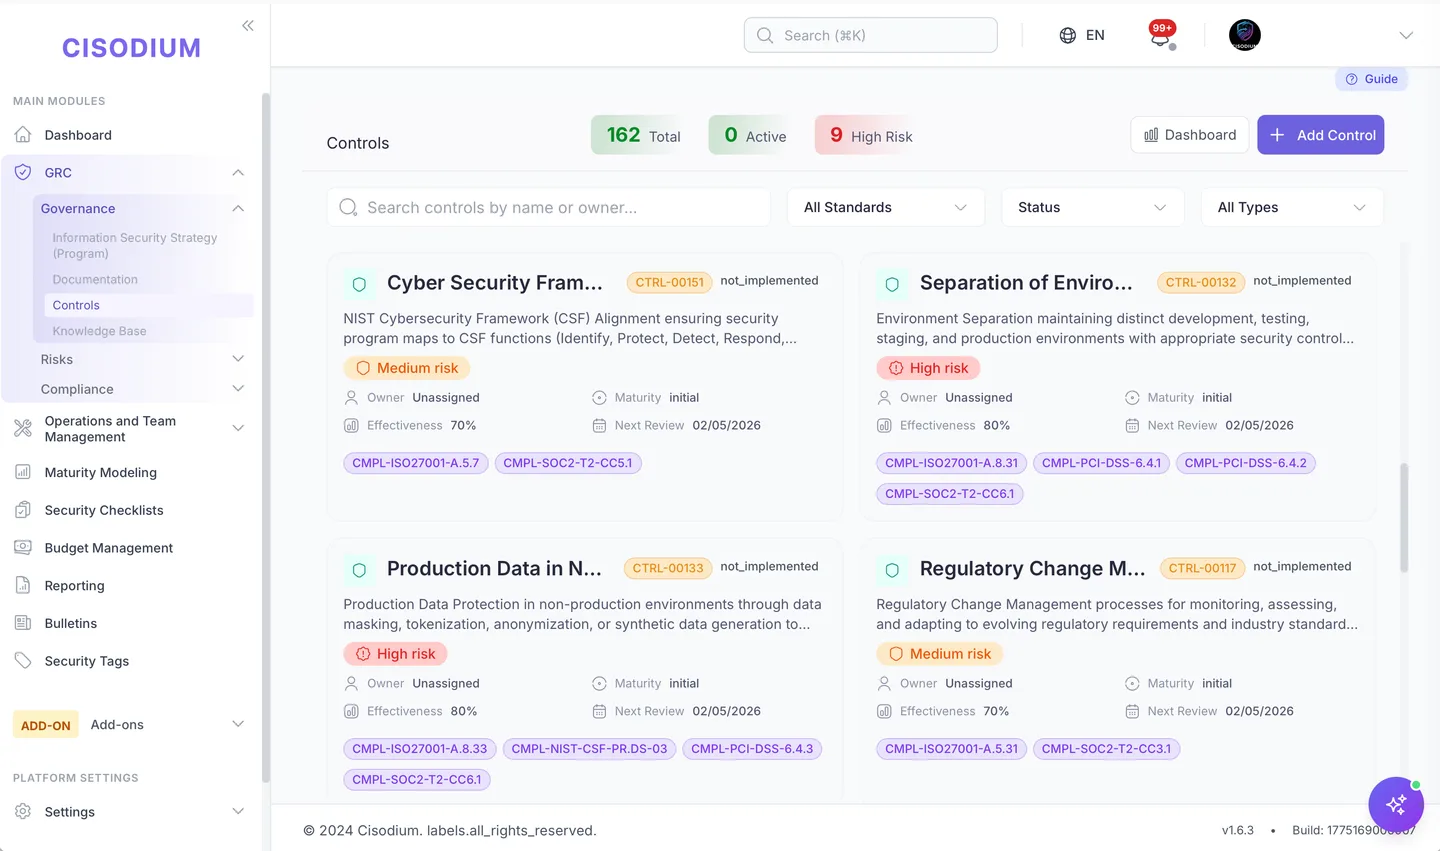
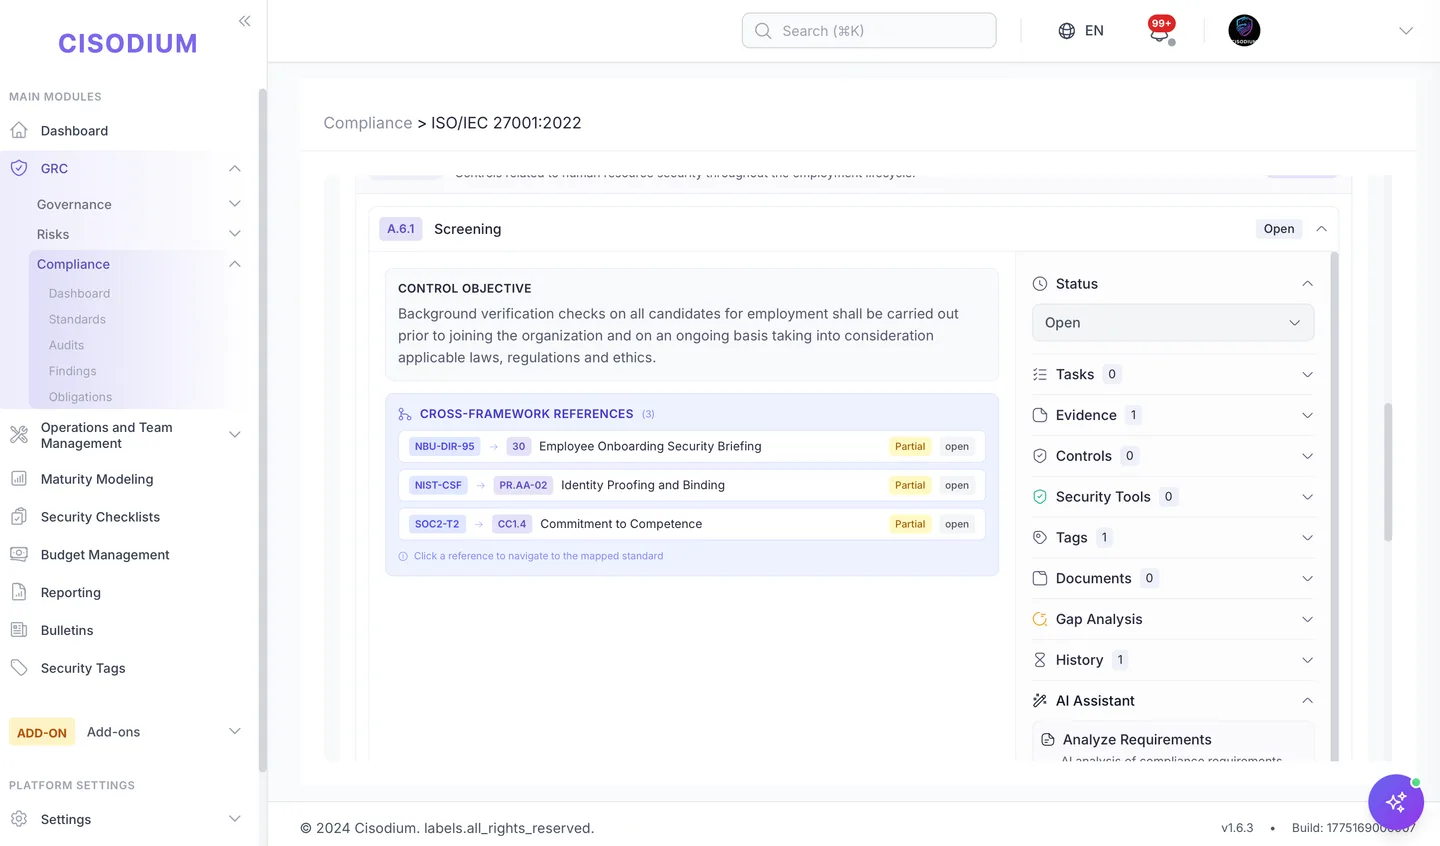 COMPLIANCECompliance OfficerMap once. Satisfy many.Map one control to several frameworks, take the audit cycle from scope to certificate upload, then close each finding against a verify step instead of an opinion.
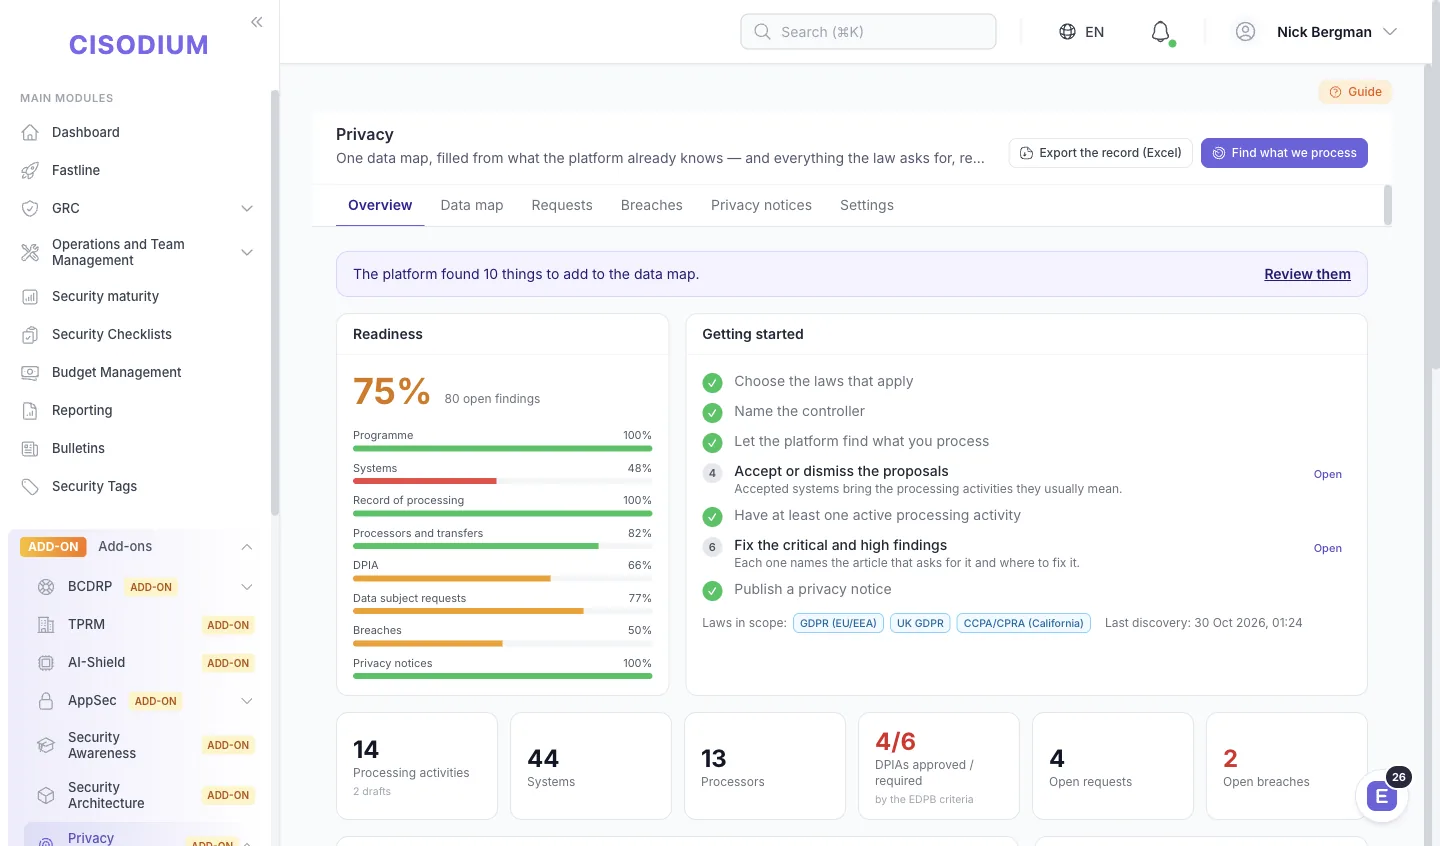 GDPRData Protection OfficerArticle 30 wants a record. Not a folder.A regulator's question should be answerable from the register itself. Article 30 entries, DPIAs, consent records and processors sit in one dataset, with data subject requests broken into tasks. Seeded in the platform as Privacy Officer — the same job under the US title.
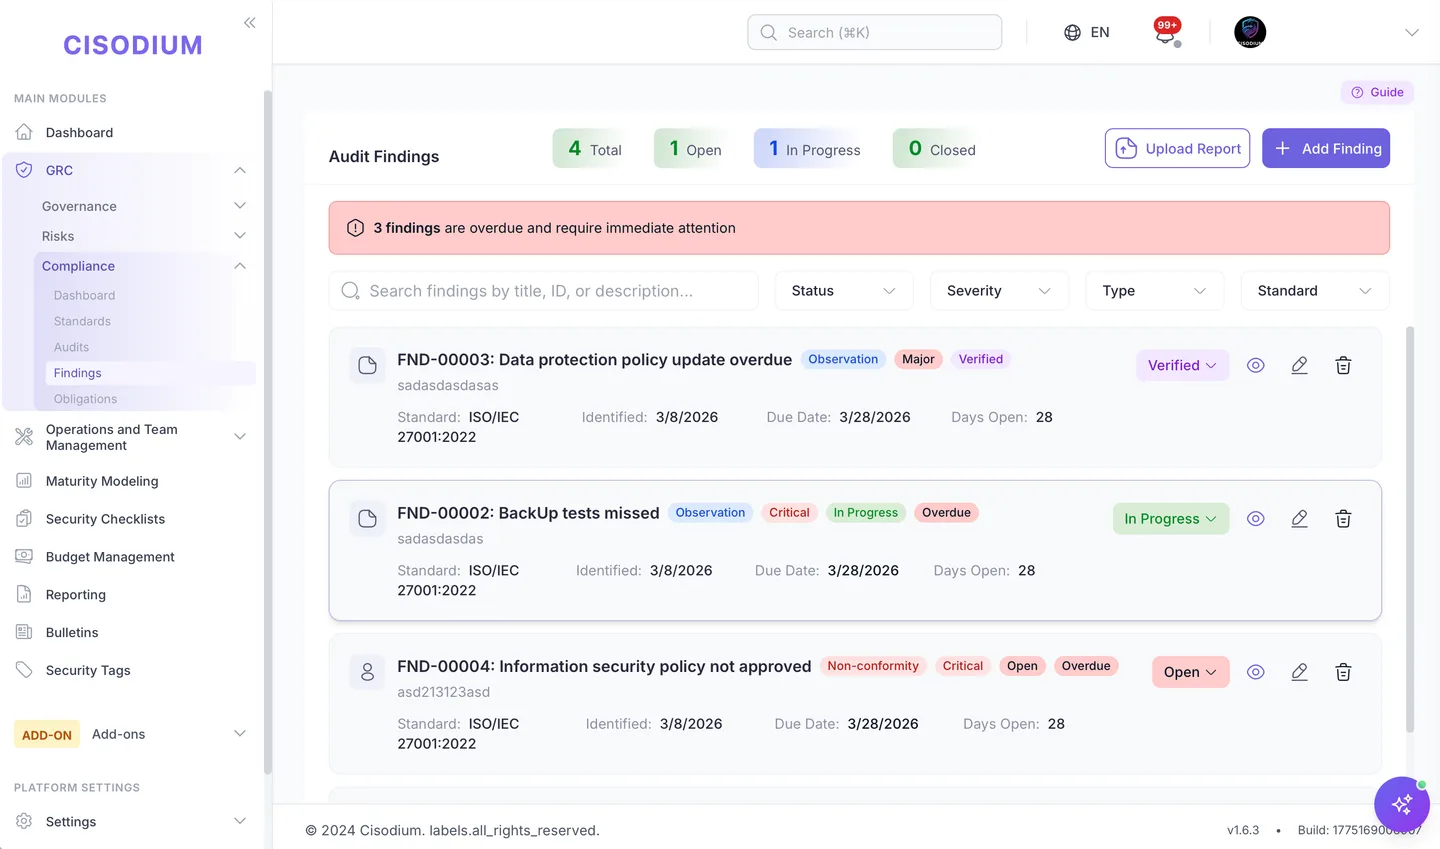 AUDITExternal AuditorAssessment quality, not logistics.Two doors lead here. A scoped read-only role for a named account reads compliance, the control library, the documents and the risk register; an invitation code opens the six-tab auditor portal with no platform account at all.
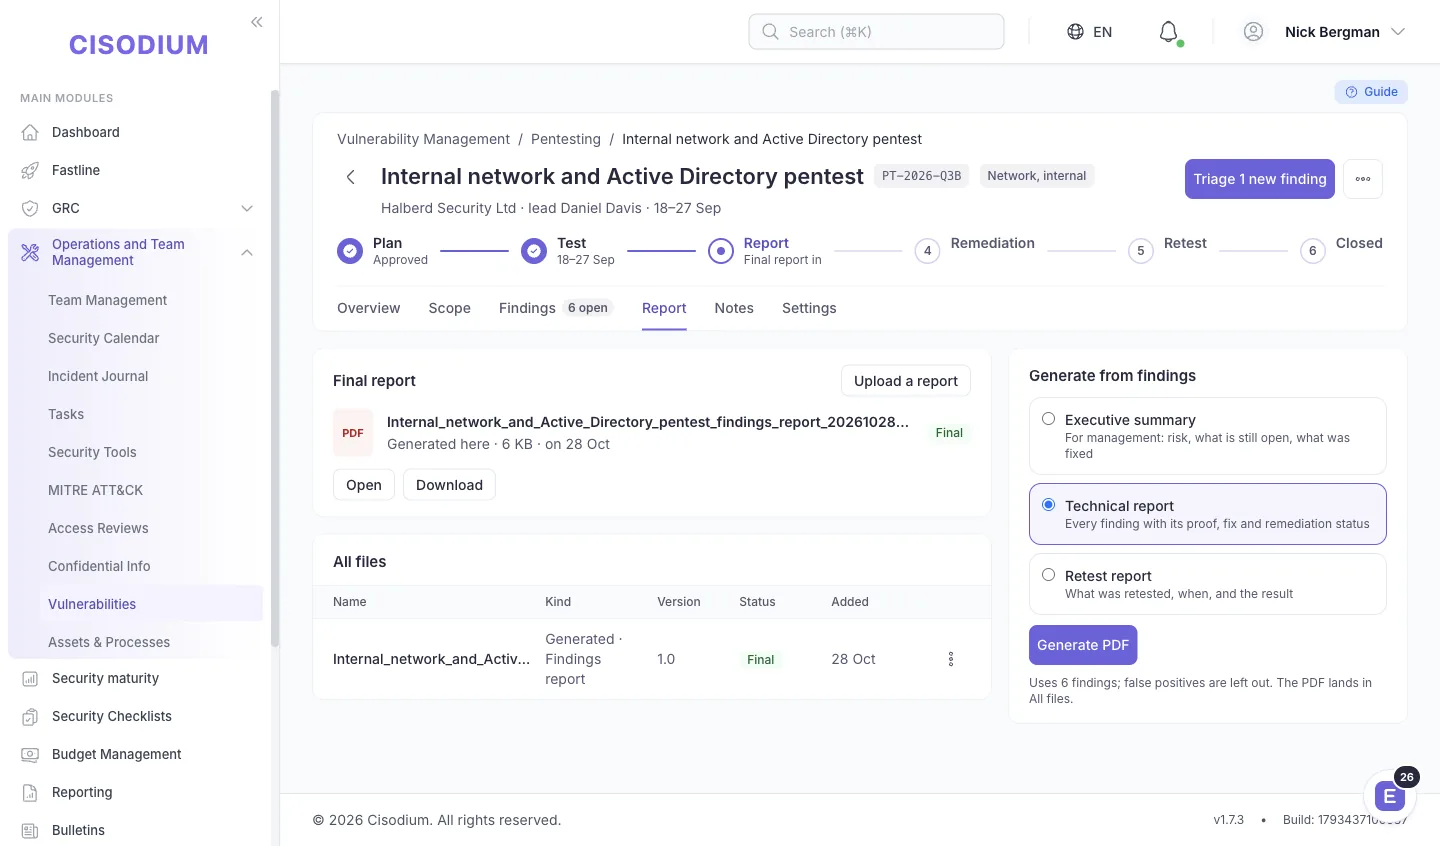 PENTESTPenetration TesterFindings where the fix happens. No PDF to re-key.Invited for one engagement: accept the rules of engagement, read the scope, record findings with proof and retest the fixes — inside the client's own workspace, within the dates and addresses they allowed.
Run the day
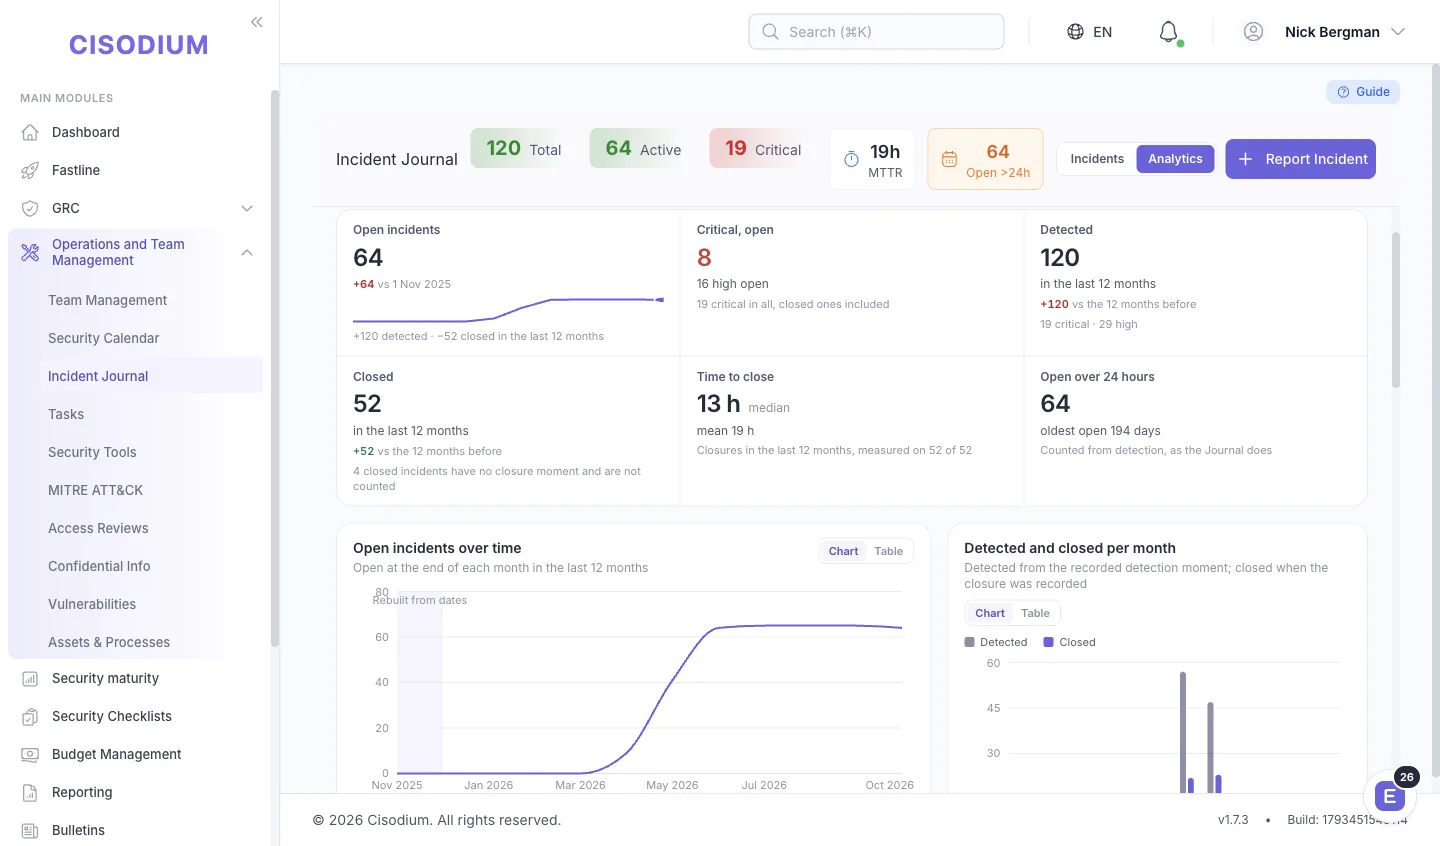 SOCSOC ManagerThe shift ends. The context does not.Continuity is the SOC's hardest problem; it dies at seven in the morning. Rota, escalation, workload and a signed handover keep it alive. Cases and incident records are yours to close — or to delete.
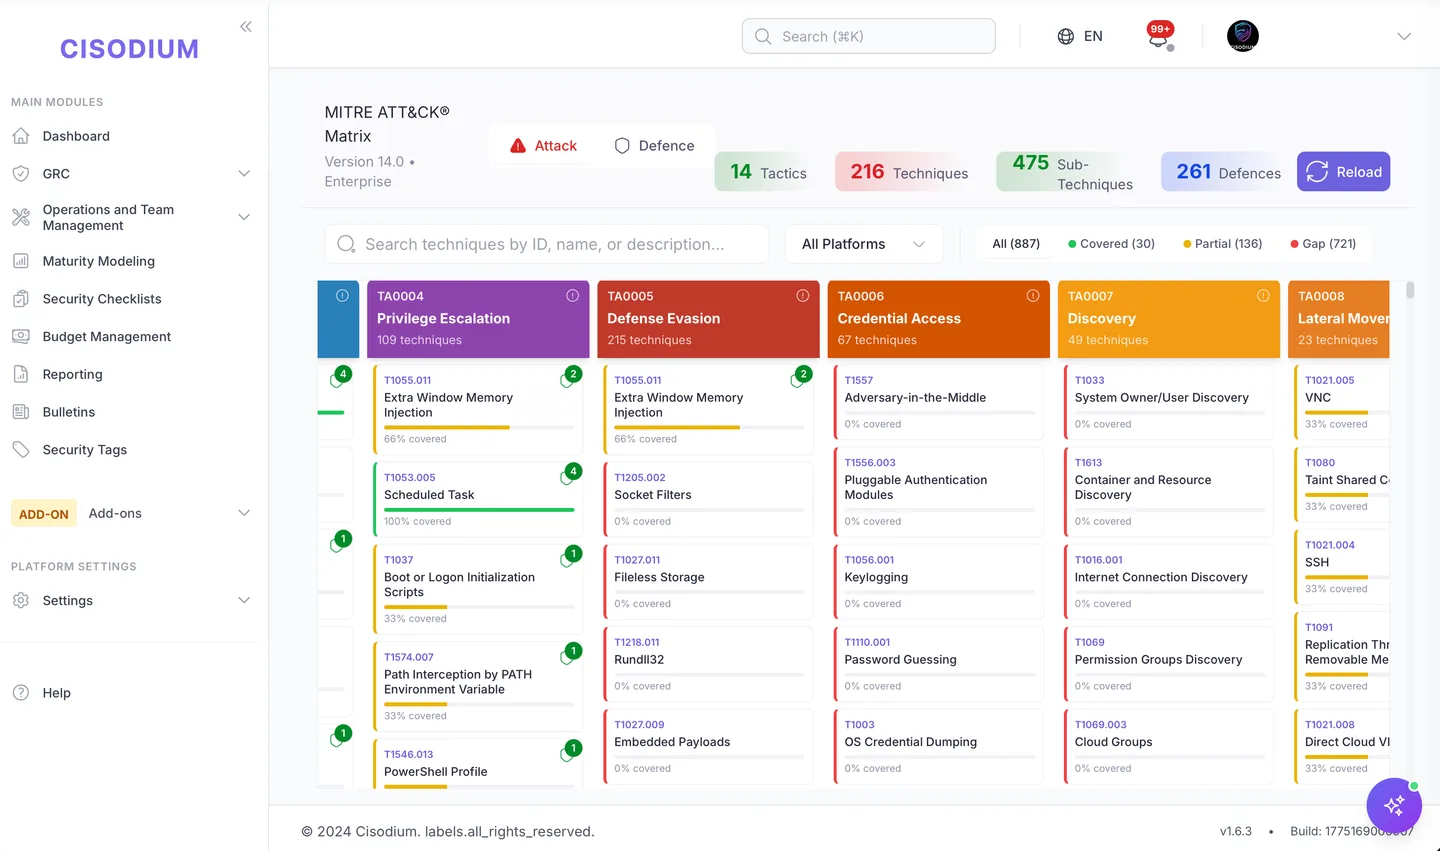 TRIAGESecurity AnalystInvestigate faster, remediate fully.Triage from the case queue, then live inside the incident record: IOCs, evidence and timeline as you go. Check whether this happened before, then hand the fix on as a task with a date on it.
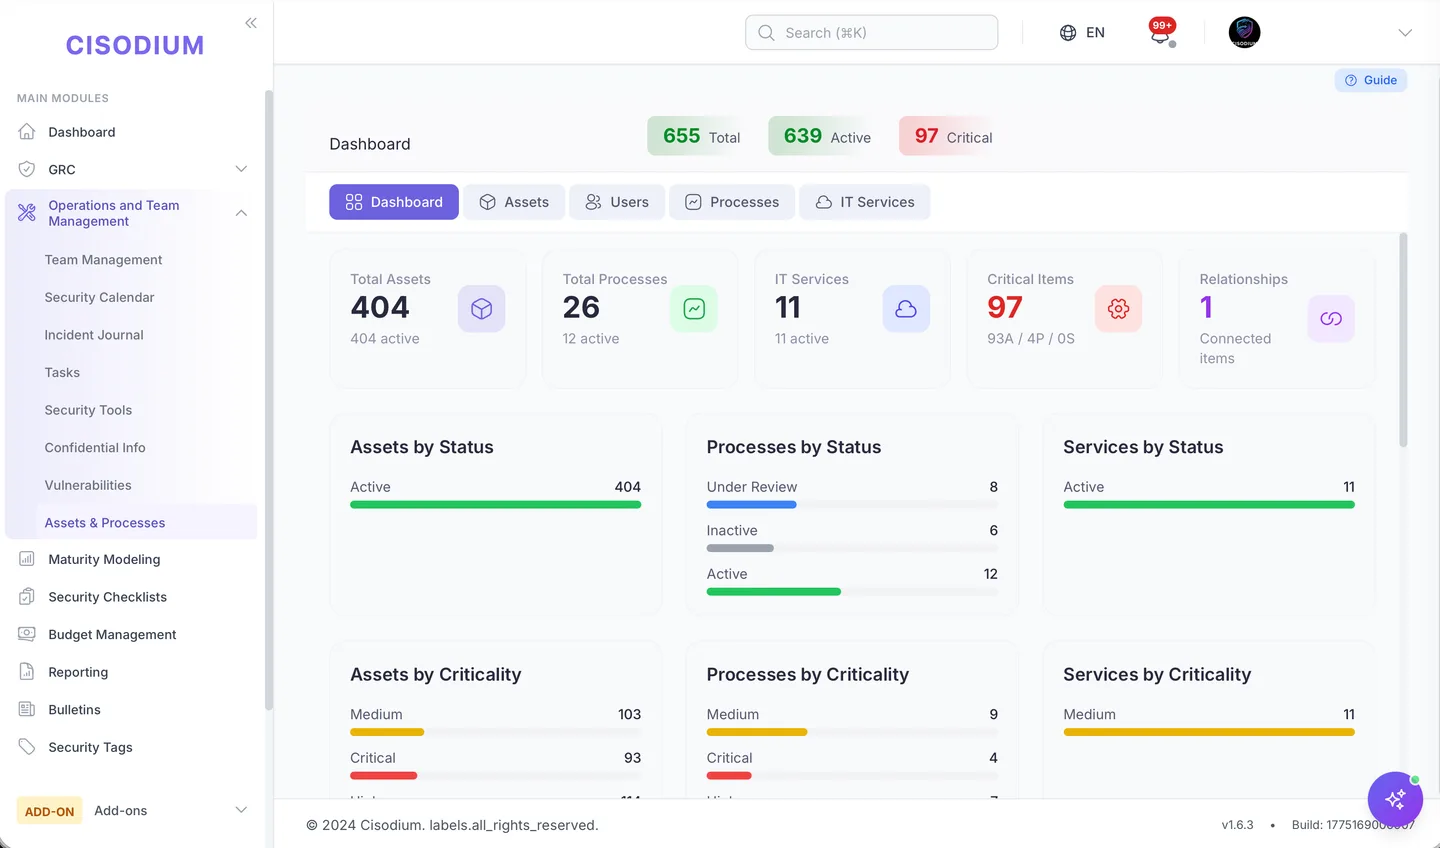 ASSETSIT ManagerPatched is a claim. Hardened is a scan.An inventory is accurate on the day it was exported. Here the register stays live, exceptions are written decisions and each system is scanned against its baseline with the hardening add-on.
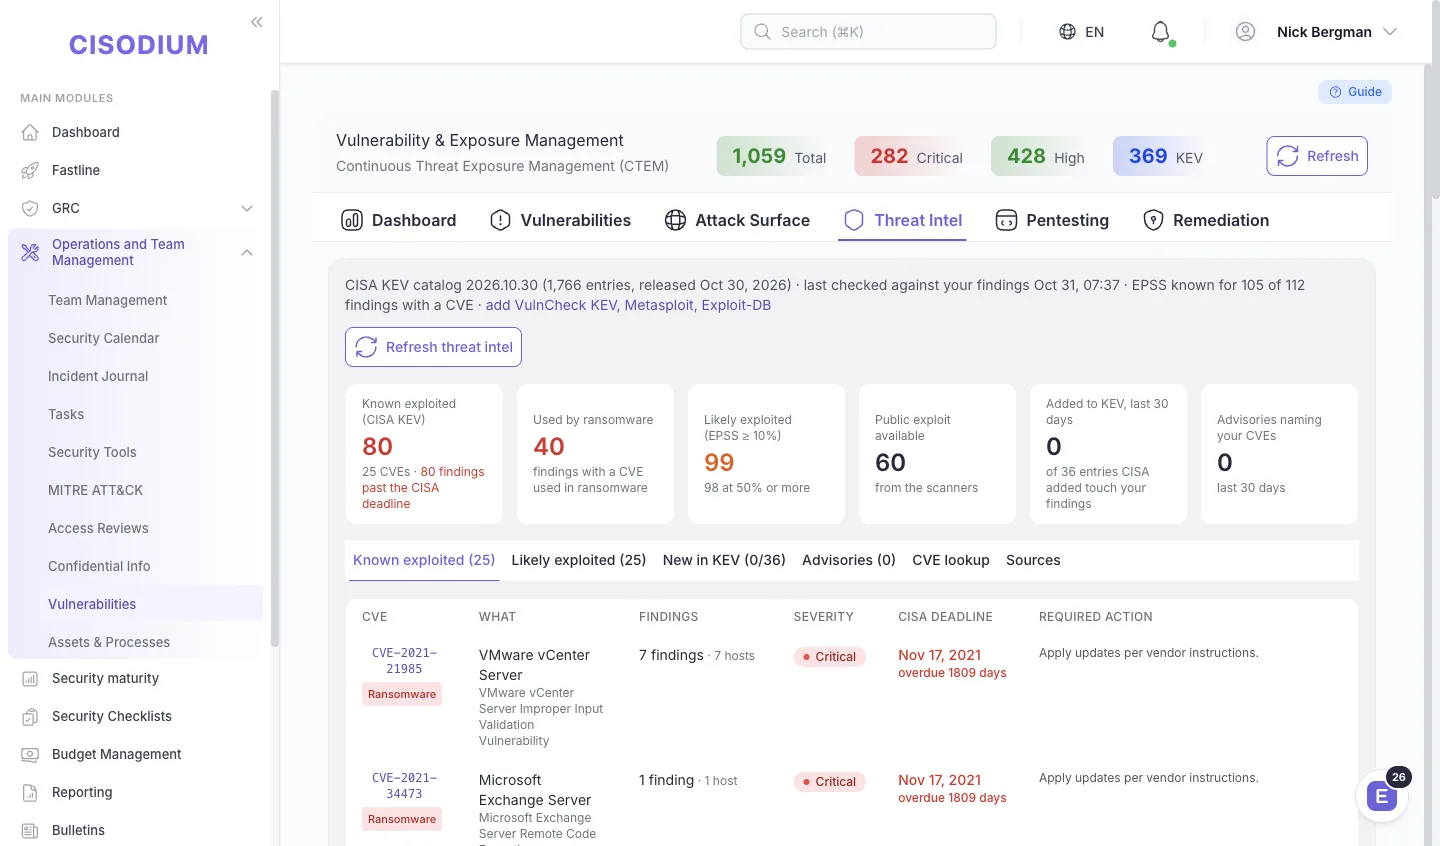 INTELThreat Intelligence AnalystForty advisories a day. Three that touch you.Public threat feeds read against your own findings: which CVEs are known exploited, which ones ransomware uses, which are likely next. Then the attack paths from an entry point to the systems that matter most.
Own a programme
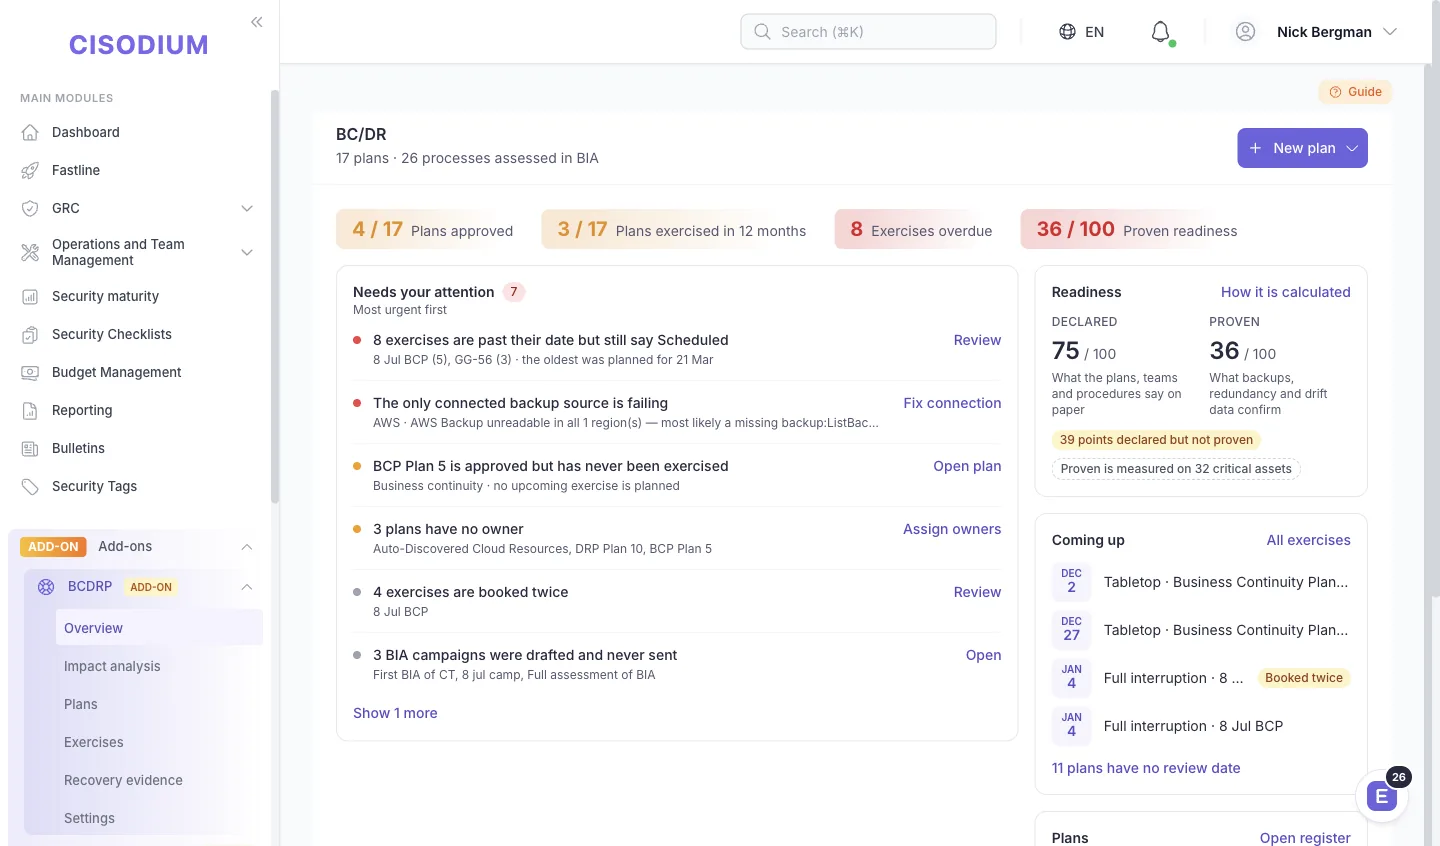 BCDRPBusiness Continuity ManagerA plan you tested. Not a plan you wrote.Process owners who never log in still have to answer the impact questionnaire. Scope the BIA as a campaign, author the plans behind it, then test them on a schedule with findings attached to every run.
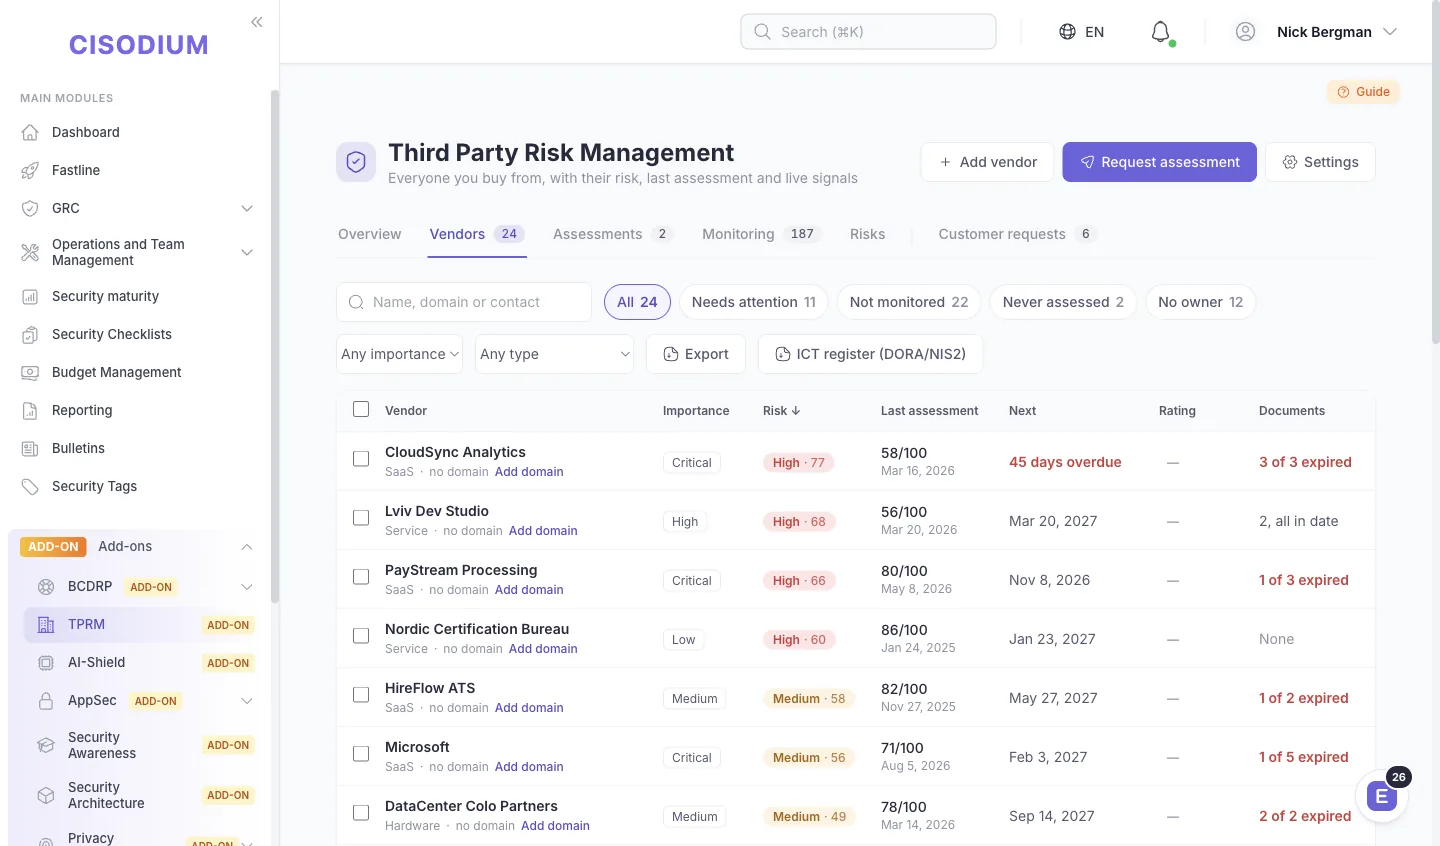 TPRMThird-Party Risk ManagerYou send the questionnaire. The calendar chases it.Vendors answer without an account, templates spawn every round and recurrence raises the next assessment on its own. What is left for you is the overdue list, worked from a pipeline rather than a memory.
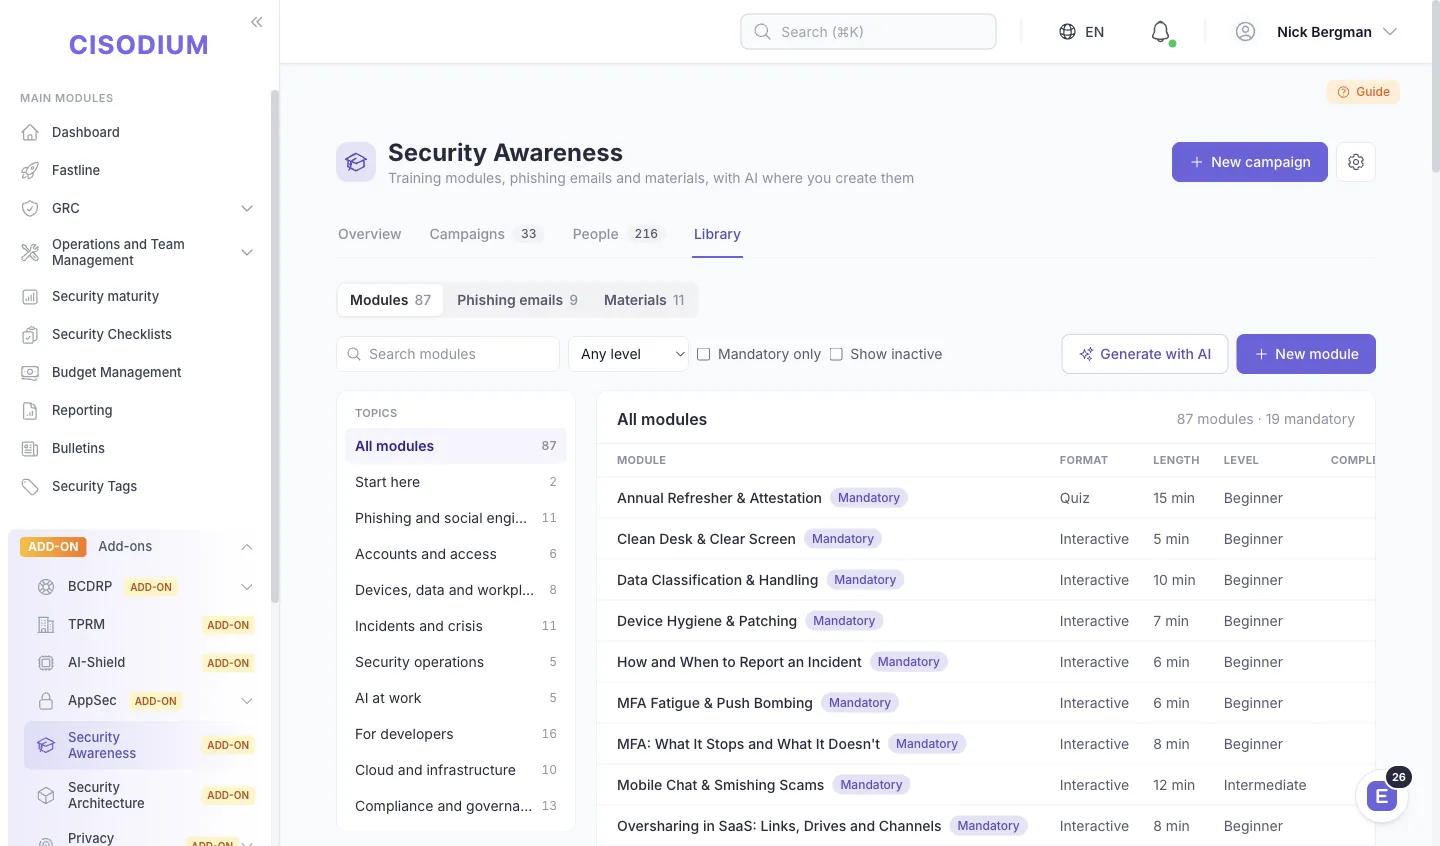 AWARENESSSecurity Awareness ManagerSent, opened, clicked, reported. All four, per person.Training that only reaches people with a login is not a programme. Modules are yours to author, enrolment goes by department and phishing runs on a recurring schedule, read per recipient rather than as one company rate.
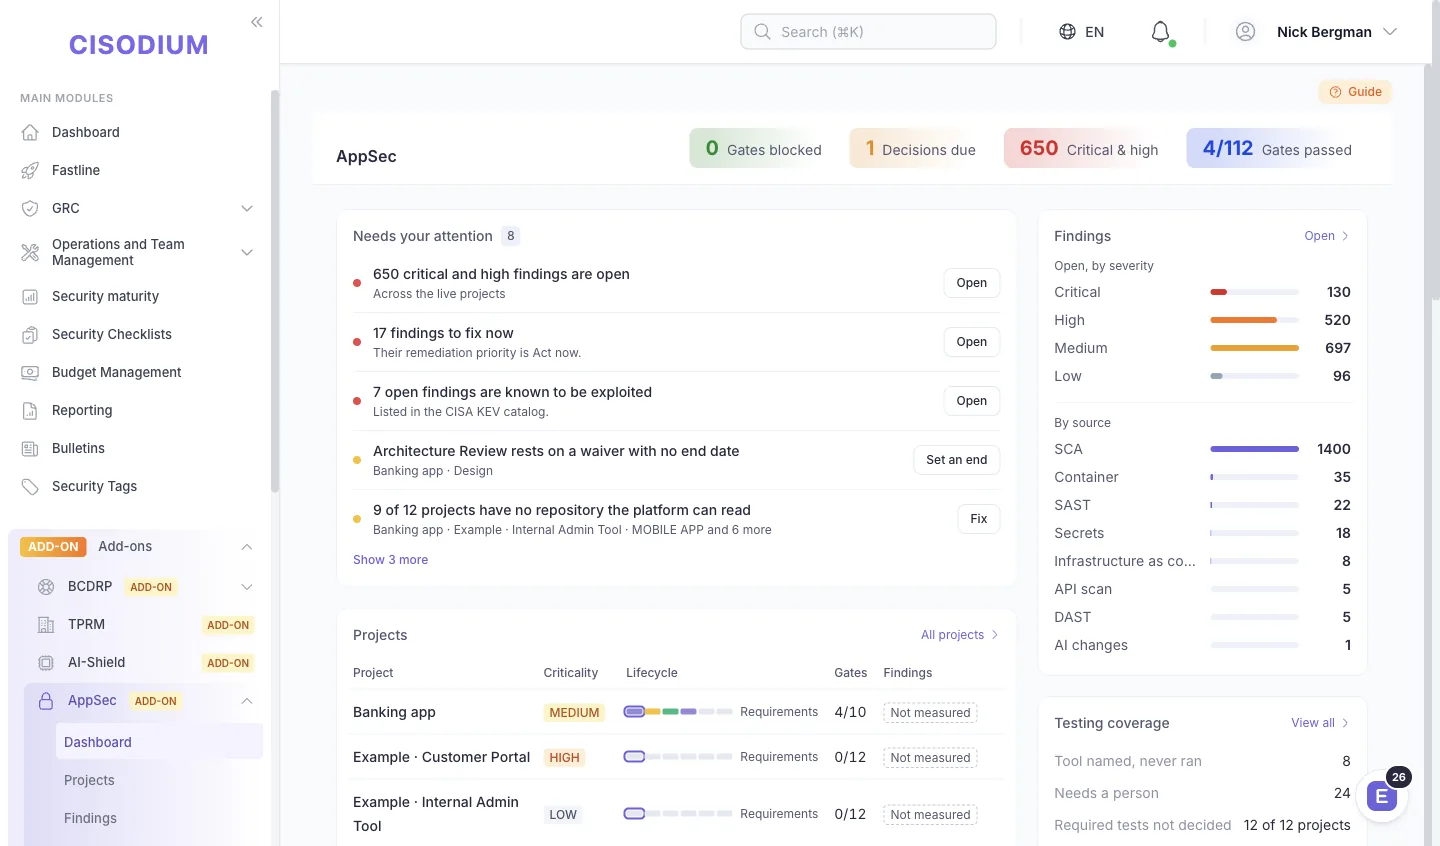 APPSECAppSec LeadOne list of what to fix. Before the release ships.Scanners, pipelines and pentests feed one register per application. Rank fixes by what is actually exploited, gate releases on rules you wrote down and keep an SBOM per release for the CRA file.
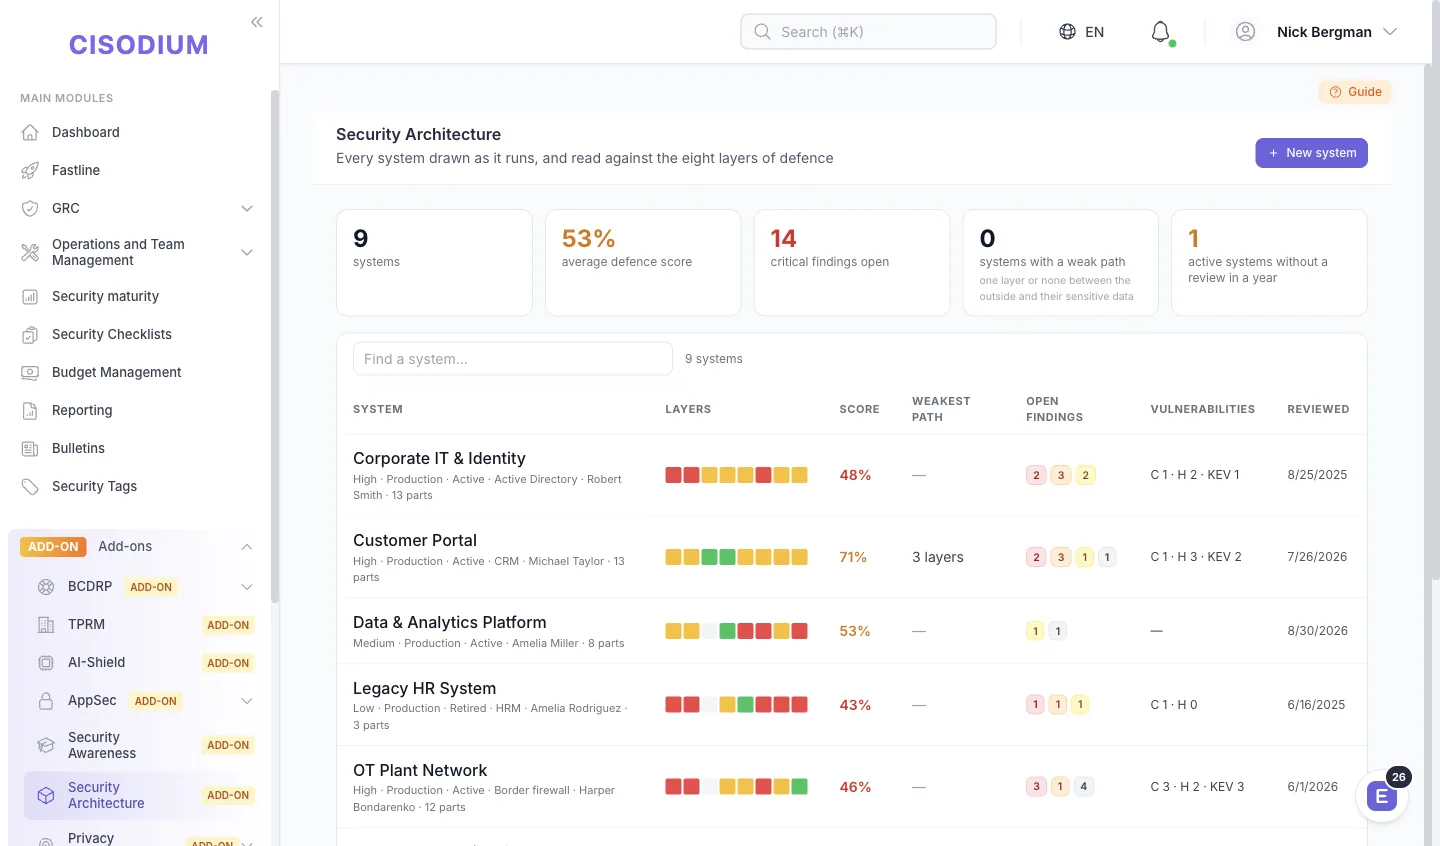 ARCHSecurity ArchitectEvery system, drawn as it runs. Every layer, scored.Draw each system as it actually runs, then read it against eight layers of defence. The thin layer, the path with one wall and the overdue design review show up before an attacker or an auditor finds them.
Who hands what to whom
Sixteen roles, one set of registers. Pick a role to see what lands on its desk and where its work goes next.
Receives
Hands over
Receives
Hands over
—
Receives
Hands over
Receives
—
Forty advisories a day. Three that touch you.
Open the role page →Hands over
Receives
Hands over
Receives
—
You send the questionnaire. The calendar chases it.
Open the role page →Hands over
Receives
A plan you tested. Not a plan you wrote.
Open the role page →Hands over
Receives
—
Every system, drawn as it runs. Every layer, scored.
Open the role page →Hands over
Receives
Hands over
—
Receives
Sent, opened, clicked, reported. All four, per person.
Open the role page →Hands over
Receives
Hands over
Receives
—
Hands over
ReceivesHands overPick a role to light up its handoffs.
Follow one piece of work
Pick a path and watch it move: who receives the work, what they do with it and who gets it next.
Receives
—
Does
Check the KEV catalogue against your own findings.Each known-exploited CVE shows the hosts it sits on and how far past the CISA deadline it runs.
Threat intelHands over
→ Security AnalystWhich CVEs are exploited now: KEV and EPSS
Receives
← Threat Intelligence AnalystWhich CVEs are exploited now: KEV and EPSS
Does
Triage and update a vulnerability.State, severity and remediation notes change from the queue itself — reading is not the limit of this role.
Vulnerability managementHands over
→ IT ManagerA task to fix the finding
Receives
← Security AnalystA task to fix the finding
Does
Turn a vulnerability into a patch task.Read the queue, raise the work item, own it to done: the queue is read-only, the task is not.
TasksHands over
→ Risk ManagerAssets and vulnerabilities to score
Receives
← IT ManagerAssets and vulnerabilities to score
Does
Move a risk through the edit wizard.Inherent score, treatment, owner and residual score change in one pass. The register never holds half an update.
Risk edit wizardHands over
→ CISORisks and acceptance decisions
Receives
← Risk ManagerRisks and acceptance decisions
Does
Schedule the board pack.Risk, compliance, incidents and budget land in one dated narrative, sent on the cadence you set.
Board packHands over
—
Roles are yours to change
78 seeded roles, 203 permissions, and your own on top. Least privilege by default — not a setting you remember to switch on.
Not on this list?
Tell us the job title on the demo form. For the industry view, see use cases.
Ready to move
beyond legacy GRC?
14-day free trial. No credit card. Cloud or on-premises.